
Industrial control systems (ICS) can be hacked through barcode scanners, researchers at cybersecurity services company IOActive said on Tuesday.
Hackers previously demonstrated that keystrokes can be remotely injected via an industrial barcode scanner into the computer the scanner is connected to, which could result in the computer getting compromised.
IOActive researchers have also been looking at industrial barcode scanners and part of their research, which they described in a blog post published on Tuesday, focuses on the scanners used by airport baggage handling systems. However, the experts warned that the same attack vector can be exploited in multiple ways and against other sectors as well.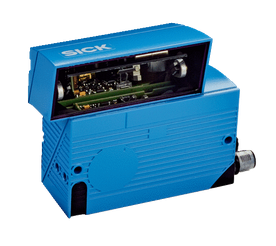
This part of the research focused on products made by SICK, a Germany-based provider of sensors for industrial automation applications, specifically on the firm’s SICK CLV65X fixed mount barcode scanners, which are usually deployed in airports for automatic baggage handling systems.
These devices can scan “profile programming” barcodes, which involve custom CODE128 barcodes. Scanning such a barcode can result in changes to the settings of a device, and this is done directly without the need for a host computer.
The problem is that this process does not involve any authentication mechanism, allowing an attacker to create a malicious barcode that, when scanned by a vulnerable scanner, causes the connected device to become inoperable, or changes its settings in an effort to facilitate further attacks.
Learn more about threats to industrial systems at SecurityWeek’s 2020 ICS Cyber Security Conferenceand SecurityWeek’s Security Summits virtual event series
IOActive researchers used reverse engineering to figure out the logic used to generate profile programming barcodes and confirmed that they are not tied to specific devices.
IOActive reported its findings to SICK in late February 2020 and the vendor released an advisory on May 31.
“An attacker with the ability to present special barcodes under his control to the affected devices, with enabled ‘profile programming’, is able to change the configuration without any authentication required,” SICK said in its advisory. “This could lead to an impact on availability, integrity and confidentiality.”
SICK has advised customers to disable the profile programming feature, which is enabled by default. The company’s advisory contains detailed instructions on how the feature can be disabled.
Related: Researchers Demo Remote Hacking of Industrial Cobots
Related: Millions of Devices Using LoRaWAN Exposed to Hacker Attacks
Related: Researchers See Improvements in Vehicle Cybersecurity






