
A researcher at IOActive discovered that home security systems from SimpliSafe are plagued by a vulnerability that allows tech savvy burglars to remotely disable the alarm without knowing the PIN.
SimpliSafe provides DIY wireless home security solutions comprised of a keypad that is used to control and configure the system, a base station, and various sensors designed to detect smoke and motion. The sensors transmit information over an ISM radio band to the base station, which maintains all system data. According to the vendor, these systems are installed in more than a million households in North America.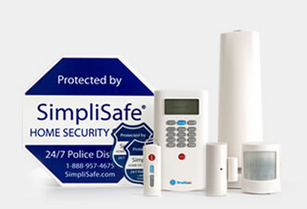
IOActive researcher Dr. Andrew Zonenberg discovered that communications between the system’s components are not protected, allowing a remote attacker to launch what is known as a replay attack. Because the radio signal transmitted from the keypad to the base station when the user disables the alarm is not encrypted, an attacker in proximity of the system can record the signal and replay it at a later time.
Using a keypad and a base station from a SimpliSafe system, and an off-the-shelf microcontroller — all of which cost roughly $250 — Zonenberg demonstrated how easy it is for a burglar to disable the alarm.
According to the expert, an attacker can hide the hacking device (which can be powered by a battery) within 100 feet of the targeted system to record the PIN transmitted when the alarm is disabled. Then, with the simple push of a button on the microcontroller, the alarm can be disarmed at any time. Zonenberg noted that an attacker needs to be in range of the targeted system; an attack cannot be conducted over the Internet.
IOActive has been attempting to report the vulnerability to the vendor since early September 2015, including via CERT, but without success. SecurityWeek has also reached out to the vendor for comment.
Even if SimpliSafe admits that its product is plagued by a serious security hole, there might not be much the company can do to address the problem without replacing existing keypads and base stations. While it would normally be easy to patch the vulnerability with a firmware update, Zonenberg says this is not an option because the microcontrollers used by the vendor are one-time programmable.
Zonenberg has pointed out that the flaw poses a serious threat because the SimpliSafe product is widespread and many owners display signs showing the use of the system, which makes it easy for burglars to identify potential targets.
Several reports have been published over the past months about vulnerabilities in home security systems. In January, Rapid7 disclosed a flaw in Comcast’s Xfinity Home Security system that could allow thieves to break into homes without triggering the alarm.
An IoT study conducted by HP last year showed that a majority of the top 10 most popular home security systems lacked protection against hacker attacks.







You must be logged in to post a comment Login