
The leak website of the LockBit ransomware operation has been taken offline by a distributed denial-of-service (DDoS) attack that appears to have been launched in response to the cybercriminals publishing data stolen from security company Entrust.
The Entrust breach was discovered on June 18 and the firm started notifying customers on July 6. However, the intrusion only came to light on July 21, when a security researcher came across a copy of the notification sent by Entrust to customers.
Some researchers said at the time that Entrust had likely fallen victim to ransomware, but no group was named. On August 18, however, the LockBit group took credit for the attack, threatening to leak all the stolen files in 24 hours unless Entrust paid a ransom.
Shortly after the black hat hackers started publishing the Entrust data, their Tor-based leak website was hit by a DDoS attack. The attack requests aimed at the LockBit website included a string urging the cybercrime group to delete the stolen Entrust data.
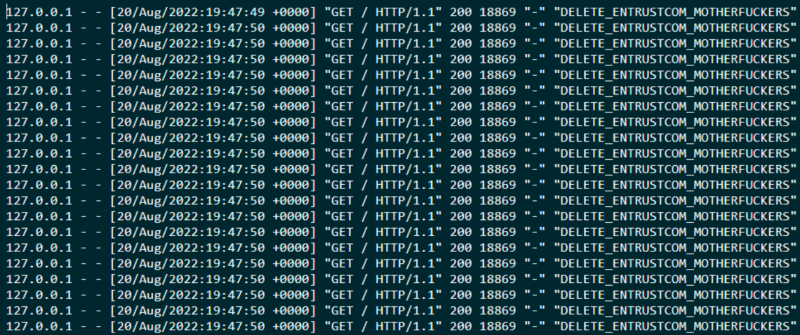
Cisco Talos researcher Azim Shukuhi said the cybercriminals claimed that they had been getting 400 requests per second from more than 1,000 servers.
It’s unclear who is behind the attack, but there has been speculation that it could be Entrust itself. The security firm has not shared any updates on the incident beyond its initial statement confirming the breach of systems used for HR, finance and marketing. The company said there was no evidence that the operation or security of its products and services was impacted.
At the time of writing, the LockBit 3.0 website appears to be mostly offline. SecurityWeek has managed to access it once and the page dedicated to Entrust displayed a message saying that LockBit operators are looking for a torrent tracker where they can upload the data stolen from the cybersecurity company. The hackers claim to have obtained 300 Gb of information.
Researcher Soufiane Tahiri has obtained a copy of what appears to be a chat between Entrust and the attackers. It shows that the hackers initially demanded a ransom of $8 million and then dropped it to $6.8 million, but the victim was only prepared to pay $1 million.
In response to the attack, the cybercrime group says it’s working on strengthening its infrastructure to protect it against future DDoS attacks and it wants to find alternative storage solutions that should allow them to leak data even if their website is disrupted. In addition, they plan on launching their own DDoS attacks against victims as part of a triple extortion model that includes file encryption, data leaks and DDoS attacks.
Related: Car Parts Giant Denso Targeted by Ransomware Group
Related: Ransomware Gang Leaks Files Stolen From Industrial Giant Parker Hannifin
Related: Ransomware Gang Threatens to Leak Files Stolen From Tire Giant Bridgestone







You must be logged in to post a comment Login