
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Data Protection

Heartbleed Still Affects 200,000 Devices: Shodan

While the number of services affected by the OpenSSL flaw known as Heartbleed has decreased, the Shodan search engine has still found nearly 200,000 vulnerable devices.

While the number of services affected by the OpenSSL flaw known as Heartbleed has decreased, the Shodan search engine has still found nearly 200,000 vulnerable devices.

Heartbleed, tracked as CVE-2014-0160, is a critical vulnerability that allows attackers to steal information protected by SSL/TLS encryption. Some researchers believe the flaw was used in an attack where hackers managed to steal 4.5 million healthcare records.

A search for vulnerable devices conducted by Shodan in November 2015 returned 238,000 results and the number dropped by roughly 1,000 by late March 2016. A new search carried out on Sunday showed that 199,594 services are still vulnerable to Heartbleed attacks.

Many of the affected devices are located in the United States (42,000), followed by South Korea (15,000), China (14,000), Germany (14,000), France, (8,700), Russia (6,600), UK (6,500), India (5,800), Brazil (5,500) and Italy (4,800). HTTPS accounts for a large majority of impacted services.
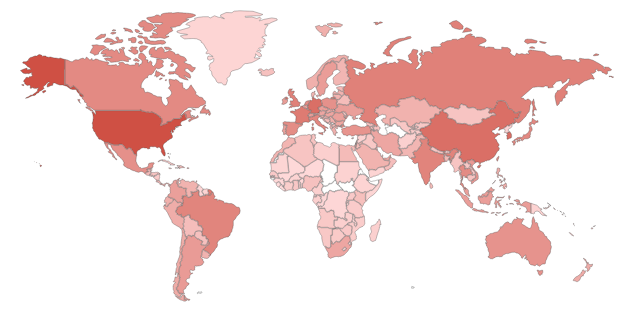
Geographical distribution of devices affected by Heartbleed

South Korea occupied only the 8th place after previous scans, but it has now become the second most affected country, apparently due to devices operated by SK Broadband, Boranet and KT Corporation (formerly Korea Telecom).

The list of top affected organizations also includes Amazon, Verizon Wireless, German ISP Strato, OVH in France, German hosting firm 1&1 Internet, Comcast, and Taiwan-based HiNet.

Advertisement. Scroll to continue reading.

Apache HTTP Server (httpd) is by far the most affected product, particularly versions 2.2.22 and 2.2.15, while the top operating system is Linux 3.x. Shodan also found that more than 70,000 of the affected services have expired SSL certificates.

Related Reading: Organizations Slow at Patching Heartbleed in VMware Deployments

Related Reading: Many Cisco Devices Still Vulnerable to NSA-Linked Exploit

Related Reading: DROWN Vulnerability Still Unpatched by Most Cloud Services

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Zeke Maldonado has been named Principal Deputy CIO at the US Department of Commerce.

FusionAuth has appointed Phil Allen as CRO.

Dave Farrow has become CISO at Bitwarden.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





