
Germany-based industrial automation company WAGO has patched several vulnerabilities in its e!DISPLAY 7300T Web Panel human-machine interface (HMI) products that can be chained to take control of affected devices.
The security holes, discovered by researchers at security consultancy SEC Consult and rated “high severity,” include multiple reflected and one stored cross-site scripting (XSS) vulnerabilities (CVE-2018-12981), unrestricted file upload and file path manipulation issues (CVE-2018-12980), and an incorrect default permissions flaw (CVE-2018-12979).
The reflected XSS flaws allow an unauthenticated attacker to execute arbitrary scripts in the context of the victim and hijack their session by getting them to click on a specially crafted link. The stored XSS can only be exploited by an authenticated hacker, but it does not require the targeted user to click on a link. Instead, the malicious code is triggered when the victim visits the “PLC List” page in the web interface.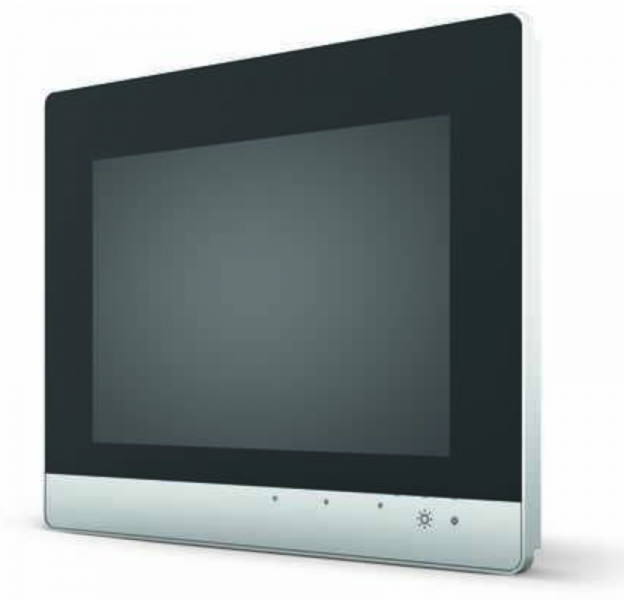
The unrestricted file upload vulnerability allows an attacker to upload arbitrary files, but not directly to the root as the web service does not run as a privileged user. On the other hand, the incorrect default permissions weakness does allow a file in the web root, specifically index.html, to be overwritten by the unprivileged “www” user.
Combining these flaws allows an attacker to upload a shell by overwriting index.html and execute arbitrary commands with the privileges of the “www” user.
“HMI displays are widely used in SCADA infrastructures. The link between their administrative (or informational) web interfaces and the users which access these interfaces is critical. The presented attacks demonstrate how simple it is to inject malicious code in order to break the security of this link by exploiting minimal user interaction,” SEC Consult explained. “As a consequence a computer which is used for HMI administration should not provide any possibility to get compromised via malicious script code.”
Register for SecurityWeek’s 2018 ICS Cyber Security Conference
The vulnerabilities impact e!DISPLAY 7300T Web Panel models 762-3000, 762-3001, 762-3002 and 762-3003 running firmware version 01. The issues have been patched by the vendor with the release of firmware version 02.
In addition to installing the latest firmware, WAGO has advised customers to restrict network access to the device and avoid connecting it directly to the Internet, restrict the number of users who can access the system, change default passwords, and avoid clicking on links from untrusted sources.
Advisories describing these vulnerabilities have been published by SEC Consult, VDE@CERT, which coordinated the disclosure of the flaws, and WAGO.
This was not the first time SEC Consult identified vulnerabilities in WAGO products. Last year, the company reported finding a potentially serious vulnerability that could give a remote attacker access to an organization’s entire network.
Related: Web Server Used in 100 ICS Products Affected by Critical Flaw
Related: CredSSP Flaw Exposes Pepperl+Fuchs HMI Devices to Attacks







You must be logged in to post a comment Login