
Researchers from Cisco’s Talos intelligence and research group have identified a dozen vulnerabilities in a wireless networking device made by Taiwan-based industrial networking, computing and automation solutions provider Moxa.
According to advisories published on Monday by both Moxa and Talos, AWK-3131A industrial AP/bridge/client devices are affected by 12 vulnerabilities that can be exploited to carry out malicious activities in an attack aimed at an organization’s industrial systems.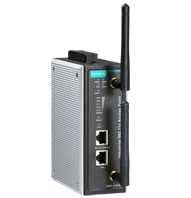
All of the vulnerabilities have been classified as critical or high severity. They can be exploited by attackers to escalate privileges to root, decrypt traffic using hardcoded cryptographic keys, inject commands and remotely control a device, run custom diagnostic scripts on the device, remotely execute arbitrary code, cause a denial-of-service (DoS) condition, and gain remote shell access to the device.
While in a majority of cases exploitation requires authentication with low privileges, some of the weaknesses can be exploited by an unauthenticated attacker.
The vulnerabilities were reported to Moxa in October and November 2019, and the vendor announced the availability of patches on February 24.
While Moxa patched these flaws fairly quickly, the company has not always been fast when it comes to addressing vulnerabilities. In December, the company urged customers to replace the discontinued AWK-3121 series AP after a researcher had identified 14 vulnerabilities in the device. However, the company had known about them since 2018 and the researcher who found the security holes had published exploits in June 2019.
This is not the first time Cisco Talos researchers have found vulnerabilities in Moxa’s AWK-3131A devices. Back in 2017, they reported finding hardcoded credentials that gave attackers full access to Moxa APs, and separately disclosed more than a dozen vulnerabilities affecting the same product.
Related: Vulnerability in ABB Plant Historian Disclosed 5 Years After Discovery
Related: Many Vulnerabilities Discovered in Moxa Industrial Switches
Related: Profinet Vulnerability Exposes Siemens, Moxa Devices to DoS Attacks







You must be logged in to post a comment Login