
A vulnerability in the popular WordPress plugin bbPress can be exploited to insert malicious JavaScript code into forum posts, web security company Sucuri has warned.
bbPress is a forum software plugin maintained by Automattic, the company behind the WordPress.com blogging service. bbPress is currently installed on more than 300,000 WordPress websites and it powers the official WordPress.org support forum.
Researchers at Sucuri discovered that the plugin is plagued by a stored cross-site scripting (XSS) vulnerability that can be easily exploited by a remote attacker to hijack user accounts and perform actions on their behalf.
The flaw is related to bbp_mention_filter, a function that finds users mentioned in a forum post using the @ symbol and links to their profile. The problem, according to experts, is that bbPress doesn’t check if mentions are already located inside an HTML tag’s attribute, which breaks the hyperlink tag and allows an attacker to insert arbitrary event handlers and execute arbitrary JavaScript code.
For example, a user named “test” can break the hyperlink tag by posting a reply containing a tag with the href attribute set to “@test.”
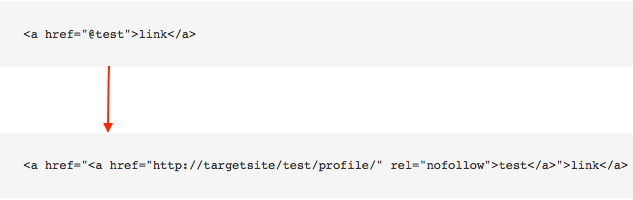
Since it’s a stored XSS vulnerability, the malicious code injected by the attacker would get executed whenever the post is viewed by a user.
The vulnerability, which affects bbPress 2.5.8 and earlier, was reported to the bbPress team on April 12 and it was patched on May 2 with the release of version 2.5.9.
“If you’re using any version of bbPress 2.x and have not yet updated, please take a moment to update your bbPress installations to 2.5.9. If you’re using WordPress’s built-in updater, it should only take a click or two,” bbPress lead developer John James Jacoby said in a blog post.
According to Sucuri, the vulnerability was similar to one found last year in Akismet, an anti-spam plugin created by Automattic.
Related: WordPress 4.4.2 Patches Open Redirect, SSRF Flaws
Related: Backdoor in WordPress Plugin Steals Admin Credentials






