
Industrial cybersecurity firm Claroty this week disclosed technical details for two potentially serious vulnerabilities affecting PowerLogic smart meters made by Schneider Electric.
PowerLogic is a line of revenue and power quality meters that are used not only by utilities, but also industrial companies, healthcare organizations, and data centers for monitoring electrical networks.
Researchers at Claroty discovered that some of the PowerLogic ION and PM series smart meters are affected by vulnerabilities that can be exploited remotely by an unauthenticated attacker by sending specially crafted TCP packets to the targeted device.
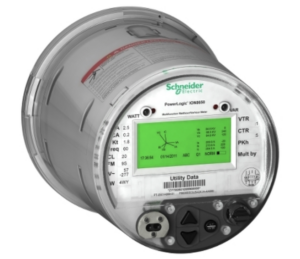 “These smart meters communicate using a proprietary ION protocol over TCP port 7700, and packets received by the device are parsed by a state machine function,” Claroty explained in a blog post. “We found that It is possible to trigger the flaw during the packet-parsing process by the main state machine function by sending a crafted request. This can be done without authentication because the request is fully parsed before it is handled or authentication is checked.”
Claroty said its researchers identified two different exploitation paths — depending on the architecture of the targeted device — and two different CVE identifiers have been assigned.
One of them, CVE-2021-22714, is considered critical as it allows an attacker to cause the targeted meter to reboot (i.e. DoS condition) and possibly even to execute arbitrary code. The other one, CVE-2021-22713, can only be exploited to force the device to reboot and it has been assigned a high severity rating.
Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series
The vulnerabilities impact several PowerLogic ION device models and one PM model. Security updates for some of the impacted devices were released in July 2020, while others were patched in January and March 2021. Some of the impacted power meters will not receive patches as they are no longer supported.
Users of the affected Schneider Electric products should apply the patches or mitigations to prevent potential attacks, particularly since information about the flaws has been made public.
Additional details about the patches and mitigations are available in the advisories (CVE-2021-22714 and CVE-2021-22713) released this week by Schneider Electric.
UPDATED: the penultimate paragraph initially mentioned risk to consumer and utilities, but the reference was removed due to PowerLogic meters being part of a B2B offer and not used by consumers
Related: Several Vulnerabilities Found in GE Power Meter Software
Related: Siemens Says Power Meters Affected by Urgent/11 Vulnerabilities
Related: ICS-CERT Issues Alerts After Expert Discloses Power Meter Flaws






