
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Endpoint Security

Microsoft Defender ATP Users Get False Positive Alerts for Mimikatz, Cobalt Strike

Microsoft rushed to take action on Wednesday after Defender Advanced Threat Protection (ATP) users reported getting Cobalt Strike and Mimikatz alerts that turned out to be false positives.

Microsoft rushed to take action on Wednesday after Defender Advanced Threat Protection (ATP) users reported getting Cobalt Strike and Mimikatz alerts that turned out to be false positives.

Cobalt Strike is a commercial penetration testing tool. However, it has often been abused by malicious actors for its advanced capabilities, including in Ryuk, Sodinokibi and other ransomware attacks.

Mimikatz is a post-exploitation tool designed for harvesting passwords from compromised systems. It too has been used by many profit-driven and state-sponsored threat groups.

It’s not surprising that some Microsoft Defender ATP users had a small heart attack on Wednesday when they saw multiple high-severity alerts for Cobalt Strike. Others reported seeing Mimikatz alerts. In both cases they turned out to be false positives.
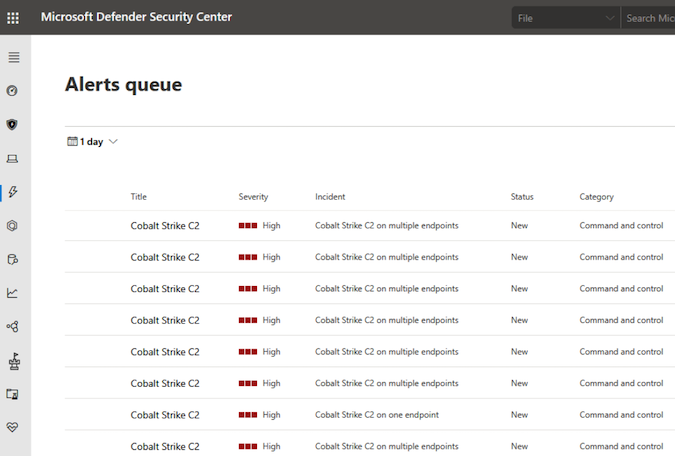
Cobalt Strike false positive in Defender ATP - Credits: @ffforward

The issue was likely caused by a bad rule pushed to Defender ATP and Microsoft addressed the issue within hours.

“We’ve addressed the issue that led to false positive alerts and corrected notifications some customers may have received,” a Microsoft spokesperson told SecurityWeek.

Advertisement. Scroll to continue reading.

However, Jon Hencinski, director of SecOps at cybersecurity company Expel and one of the people who monitored the incident, advised organizations not to immediately dismiss Cobalt Strike alerts in Defender ATP and instead follow their triage process as normal.

Related: Microsoft Rushes to Fix Bug That Broke Windows Defender Scans

Related: Microsoft Pulls UEFI-Related Windows Update After Users Report Problems

Related: New VirusTotal Service Aims to Reduce False Positives

Related: Users Unable to Log on to Windows Due to McAfee Update

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Zeke Maldonado has been named Principal Deputy CIO at the US Department of Commerce.

FusionAuth has appointed Phil Allen as CRO.

Dave Farrow has become CISO at Bitwarden.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





