
The Dridex botnet operators have recently changed the delivery mechanism in their spam campaigns, as well as the payload, to deliver the Locky ransomware, researchers at Trustwave warn.
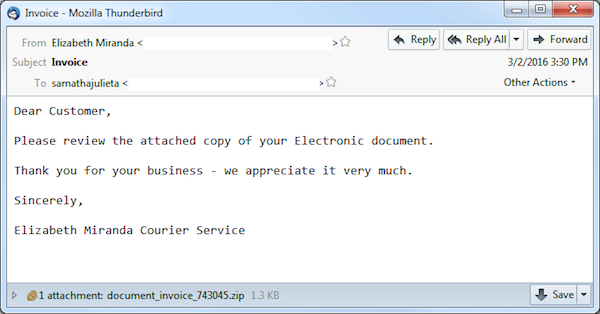
The security firm has observed a massive spam campaign of over 4 million malware spams, with malware accounting for 18 percent of the total spam detected. A recent blog post from TrustWave’s Rodel Mendrez also reveals that the campaign was not continuous, but done it concentrated bursts, with peaks of 200K emails hitting servers in a single hour.
Although the spam came from the same botnet used to spread Dridex via documents with malicious macros, the threat actors behind the campaign have changed the distribution mechanism to use JavaScript (.js) attachments. Additionally, the cybercriminals have changed the end malware being used, which is now the Locky ransomware. Dridex and Locky were said before to be connected, with a notable similarity in tactics when both switched to using Form object in macros to obfuscate their malicious code.
Once installed on a target computer, Locky reports back the infected systems information, then starts to encrypt files that have certain extensions, including those on unmapped network shares. It also renames the encrypted files to a random name and uses .locky as the file extension and drops ransom notes in encrypted folders and on the desktop.
Each Locky victim is directed to a unique webpage that can only be accessed through Tor anonymous browser. On that page, the victim finds bitcoin payment information, along with details on how they can get the decrypter tool.
In early February, researchers at FireEye revealed that the cybercriminals behind the Dridex botnet ramped up their activity following a short holiday season break. In January, IBM X-Force researchers discovered that new Dridex variants borrowed a redirection attack scheme concept from the Dyre Trojan, which has been inactive since November 2015.
According to a recent report from Fortinet, despite emerging on the threat landscape in mid-February, Locky needed only two weeks to become the second top ransomware on the charts, accounting for 16.47 percent of all ransomware attacks. CryptoWall remains the top threat with 83.45 percent of the total 18.6 million hits collected by Fortinet from the three major ransomware families between Feb. 17 and Mar. 2.






You must be logged in to post a comment Login