
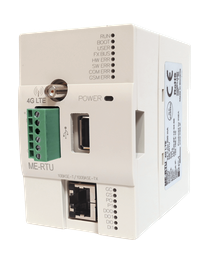
A critical vulnerability found in a remote terminal unit (RTU) made by Slovenia-based industrial automation company Inea can expose industrial organizations to remote hacker attacks.
The existence of the vulnerability came to light last week, when the US Cybersecurity and Infrastructure Security Agency (CISA) published an advisory to inform organizations. The vendor has released a firmware update that patches the issue.
The security hole, tracked as CVE-2023-2131 with a CVSS score of 10, impacts Inea ME RTUs running firmware versions prior to 3.36. This OS command injection bug could allow remote code execution, CISA said.
The impacted product provides a data interface between remote field devices and the control center through a cellular network. According to CISA, the product is used worldwide in industries such as energy, transportation, and water and wastewater.
The vulnerability was discovered and responsibly disclosed by Floris Hendriks, a researcher who is working on getting his master’s degree in cybersecurity at the Radboud University in the Netherlands.
Hendriks found the vulnerability as part of a bigger research project into the security of ICS remote management devices. He and another researcher from Radboud University were recently credited by CISA for serious flaws found in Contec and Control By Web products.
As part of this project, Hendriks has developed a method for discovering devices using the Censys search engine. Once devices are identified online, their firmware is analyzed for vulnerabilities.
The researcher told SecurityWeek that the Inea RTU vulnerability can be exploited without authentication directly from the internet. He has identified a couple of internet-exposed devices.
“The exploit can be run from the public internet, the attacker does not have to be on the local network,” Hendriks explained.
Learn More at SecurityWeek’s ICS Cyber Security Conference
The leading global conference series for Operations, Control Systems and OT/IT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
October 23-26, 2023 | Atlanta
www.icscybersecurityconference.com
Exploitation of CVE-2023-2131 can result in the attacker gaining root privileges on the targeted RTU, which gives them complete control of the device. The potential impact in a real world scenario depends on what the RTU is used for, but the flaw could allow an attacker to cause disruption.
“It is an RTU, which means that it is a device that sits between the SCADA and the instrumentation devices,” he explained. “As you can control the RTU, you can change both the input and outputs. It depends on what the organization uses the RTU for, but if it is used to, for example, open/close pumps or a water gate then the attacker is able to control that as well.”
“The attacker is also able to crash the system, which can have an enormous impact on the industrial processes of an organization,” the researcher added. “An attacker can also use it for network pivoting, to get, for example, access to the local network of the organization.”
Related: High-Severity Vulnerabilities Found in WellinTech Industrial Data Historian
Related: Irrigation Systems in Israel Disrupted by Hacker Attacks on ICS
Related: Unpatched Security Flaws Expose Water Pump Controllers to Remote Hacker Attacks







You must be logged in to post a comment Login