
The Forum of Incident Response and Security Team (FIRST) announced on Thursday the release of Traffic Light Protocol version 2.0, which brings important updates to the widely used sensitive information classification system.
The Traffic Light Protocol (TLP) was established by the UK’s National Infrastructure Security Co-ordination Center (NISCC) in 1999, and FIRST released its first version of TLP in August 2016. In 2019, a special interest group comprising more than 50 industry professionals started working on improving the TLP content, language, accessibility and supporting materials. The result of their work is TLP 2.0, which FIRST officially launched on August 5, 2022.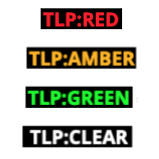
The TLP defines labels for indicating whether and how much sensitive information can be shared. The four labels are TLP:RED (for the individual recipient only), TLP:AMBER (can be distributed on a need-to-know basis with the organization and its clients), TLP:GREEN (can be shared within the community), and TLP:CLEAR (no limit on disclosure).
TLP:CLEAR was named TLP:WHITE in the previous version of the protocol. TLP 2.0 also includes the TLP:AMBER+Strict label, which is used for information that is restricted to the recipient’s organization only and it cannot be shared with clients.
TLP 2.0 also removes synonyms and colloquialisms in an effort to make translations easier and to improve accessibility for non-native English speakers. The updated version also has more consistent language and terminology, as well as some new definitions.
Another modification is related to the introduction of RGB, CMYK and HEX color codes for font and background, with recommendations for accommodating people with low vision.
FIRST, which is also in charge of the Common Vulnerability Scoring System (CVSS), pointed out that some of the changes introduced by TLP 2.0 could cause issues for current tools and firmware, but the organization is hoping for it to be fully in use by January 2023.
“We are increasingly spreading more confidential and sensitive information inside our community, inside companies, inside business sectors, inside countries, and worldwide,” said Don Stikvoort of the Open CSIRT Foundation, one of the people involved in the development of TLP 2.0. “We need systems that are easy to use, simple to understand, and straightforward enough that translation does not impact the meaning to ensure that we share sensitive information with the appropriate audience. The updated and modernized TLP version 2.0 does just that.”
Related: FIRST Announces CVSS Version 3.1
Related: NIST Releases New macOS Security Guidance for Organizations
Related: PCI Data Security Standard v4.0 Released to Address Emerging Threats






