
Several critical vulnerabilities found by Cisco Talos researchers in programmable logic controllers (PLCs) made by WAGO can be exploited remotely for arbitrary code execution and denial-of-service (DoS) attacks.
All of the flaws found by Cisco Talos affect the protocol handling code of the I/O Check configuration service used by WAGO PFC100 and PFC200 series PLCs. They were reported to the vendor in late July.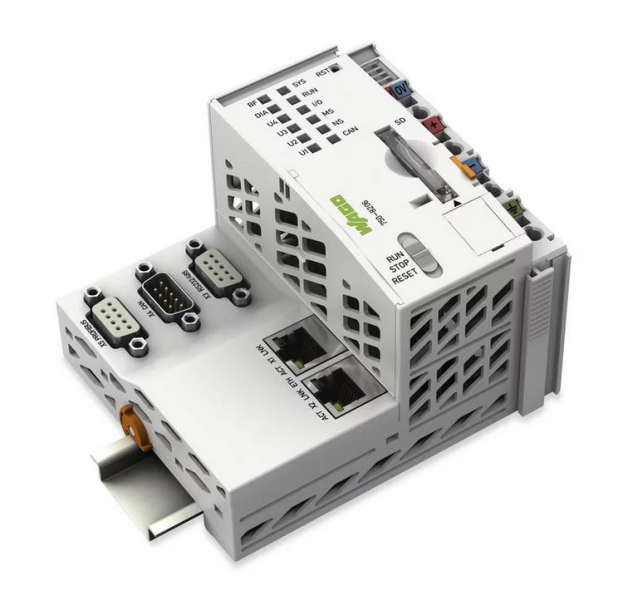
Of the total of nine vulnerabilities discovered by Talos, eight have been assigned CVSS scores of 9.8 or 10, which puts them in the critical severity category. The remaining flaw can be leveraged to obtain information and it has been rated medium severity.
The critical vulnerabilities, many of which are caused by buffer overflows, can allow a remote, unauthenticated attacker to execute arbitrary code on the device or cause a DoS condition by sending specially crafted packets. One of the DoS flaws can cause the device to restore factory settings, which results in a known default password being set.
Talos told SecurityWeek that is has found no evidence that the weaknesses have been exploited in the wild, but the company could not say if there are any exposed devices that hackers could target directly from the internet.
SecurityWeek has reached out to WAGO for comment, but the company has yet to respond.
Germany’s CERT@VDE has also published an advisory for the WAGO PLC vulnerabilities and the organization says six of the flaws have been addressed by the vendor with a firmware update.
Organizations using the impacted PLCs can also prevent attacks by disabling the port used by the I/O-Check service (port 6626) after commissioning — CERT@VDE says the problematic service is only needed during installation and commissioning of the devices, but not during normal operations.
Related: Critical Flaw in WAGO PLC Exposes Organizations to Attacks
Related: Critical Vulnerabilities Found in WAGO Industrial Switches
Related: Hackers Can Chain Multiple Flaws to Attack WAGO HMI Devices






