
Vulnerabilities discovered by researchers in some of Schneider Electric’s Easergy relays can allow hackers to disable protections for electrical networks. The vendor has released patches that should address the security flaws.
Three high-severity vulnerabilities have been found in Easergy medium-voltage protection relays — two impact Easergy P5 devices and one affects Easergy P3 devices. Schneider Electric informed customers about these vulnerabilities in January and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued an advisory last week.
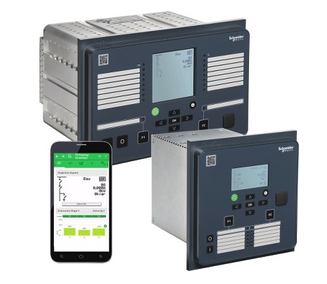 According to the advisories from Schneider and CISA, P3 relays are affected by a buffer overflow (CVE-2022-22725) that can lead to arbitrary code execution or a denial-of-service (DoS) condition if specially crafted packets are sent to the targeted device over the network.
An attacker could exploit the security hole to cause the relay to reboot, or they can gain full control of the device.
Easergy P5 relays are also affected by a buffer overflow (CVE-2022-22723) that can allow an attacker to cause program crashes and achieve code execution using specially crafted packets sent over the network. These devices also have hardcoded credentials (CVE-2022-22722) that can pose a security risk.
“If an attacker were to obtain the SSH cryptographic key for the device and take active control of the local operational network connected to the product they could potentially observe and manipulate traffic associated with product configuration,” Schneider explained.
The vendor warned in its advisories that exploitation could “result in loss of protection to your electrical network.”
Schneider Electric has credited several researchers from embedded security solutions provider Red Balloon Security for reporting the vulnerabilities.
Ang Cui, CEO at Red Balloon Security, told SecurityWeek that the affected relays are typically not exposed to the internet, and even if internet-exposed systems are found, they are likely used for demonstration purposes, rather than real-world applications.
“However, multiple cases have shown enterprise systems, remote access systems and industrial control rooms can be reached from the internet via phishing, discovered remote access credentials, and other attacks. From the control room, it is an easy, direct step to these relays,” Cui explained.
He added, “In addition, since substations are so distributed and numerous, maintaining physical security for all of them can be challenging. This means attackers could still take a more conventional approach and breach a physical security perimeter to access the relays directly.”
Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference
According to Cui, an attacker whose goal is to disrupt a large plant or the electrical grid could acquire such an Easergy relay for a few thousand dollars and analyze it in an effort to find vulnerabilities. Once they have identified flaws that they can exploit, hackers can try to gain access to the grid or plant network through established methods, such as spear-phishing or by acquiring access from specialized access brokers.
“Once able to access and compromise actual devices in the field, an attacker could disable the power supply or disrupt it in a way that causes damage to other equipment (for example, by causing backup power to rapidly cycle on and off),” Cui said. “Alternatively, they could disable the protection functions, thereby removing the protections needed in the event of a storm or the failure of another connected device (such as a transformer overload). In either case, the attacker could inflict considerable damage, and greatly increase the time and cost needed to repair systems after a fault.”
Related: Critical Vulnerability Can Be Exploited to Hack Schneider Electric’s Modicon PLCs
Related: ICS Patch Tuesday: Siemens, Schneider Electric Address Nearly 50 Vulnerabilities
Related: Another Stuxnet-Style Vulnerability Found in Schneider Electric Software







You must be logged in to post a comment Login