Researchers at Tel Aviv University have demonstrated a method of stealing encryption keys from a PC using a radio receiver small enough to hide inside a piece of pita bread.
In a paper, the researchers outlined new side-channel attacks on RSA and ElGamal implementations that use the popular sliding window or fixed window modular exponentiation algorithms. The attacks can extract decryption keys using a low measurement bandwidth even when attacking multi-GHz CPUs, the researchers found.
“We demonstrate the extraction of secret decryption keys from laptop computers, by nonintrusively measuring electromagnetic emanations for a few seconds from a distance of 50 cm,” the researchers explained in an online summary of the paper. “The attack can be executed using cheap and readily-available equipment: a consumer-grade radio receiver or a Software Defined Radio USB dongle. The setup is compact and can operate untethered; it can be easily concealed, e.g., inside pita bread.”
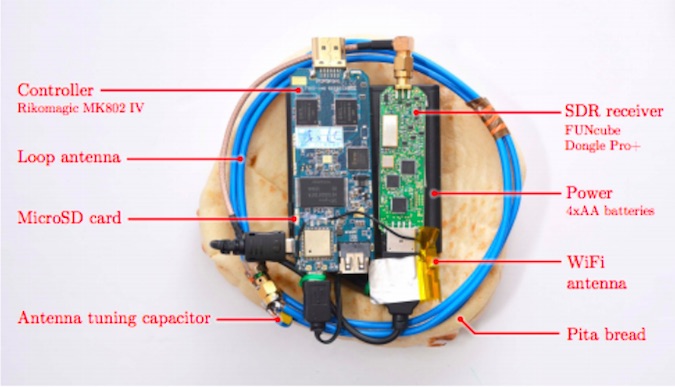
In an apparent nod to that fact, the team named their device the ‘Portable Instrument for Trace Acquisition’ (PITA). The researchers said they successfully extracted keys from laptops of various models running GnuPG within a few seconds.
“The attack sends a few carefully-crafted ciphertexts, and when these are decrypted by the target computer, they trigger the occurrence of specially-structured values inside the decryption software,” according to the researchers. “These special values cause observable fluctuations in the electromagnetic field surrounding the laptop, in a way that depends on the pattern of key bits (specifically, the key-bits window in the exponentiation routine). The secret key can be deduced from these fluctuations, through signal processing and cryptanalysis.”
The good news, blogged security researcher Graham Cluley, is that the gadget has to be very close to the target PC.
“In fact, even when the setup is enhanced with more powerful antennae, the researchers only found that they could steal the crypto-keys from a distance of 50 [centimeters], although it is possible to imagine that more expensive (and bulkier) hardware could extend the range further,” he wrote. “What is impressive is not so much the stealing of the encryption keys, but the fact that they devised such a simple, cheap and portable way to do it.”
The paper has been published online (PDF).