
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Ransomware

Ransomware Group Claims Theft of Valuable SpaceX Data From Contractor

The LockBit ransomware group claims to have stolen valuable SpaceX data after breaching the systems of Maximum Industries.

The LockBit ransomware group claims to have stolen valuable SpaceX files after breaching the systems of piece part production company Maximum Industries.

The Texas-based Maximum Industries specializes in waterjet and laser cutting and CNC machining services, and advertises itself as a contract manufacturing facility. 

The LockBit hackers claim Elon Musk’s rocket and spacecraft maker SpaceX uses Maximum Industries services. They also claim that on Maximum Industries’ systems they found roughly 3,000 “drawings certified by space-x engineers”, which they plan on selling through an auction.
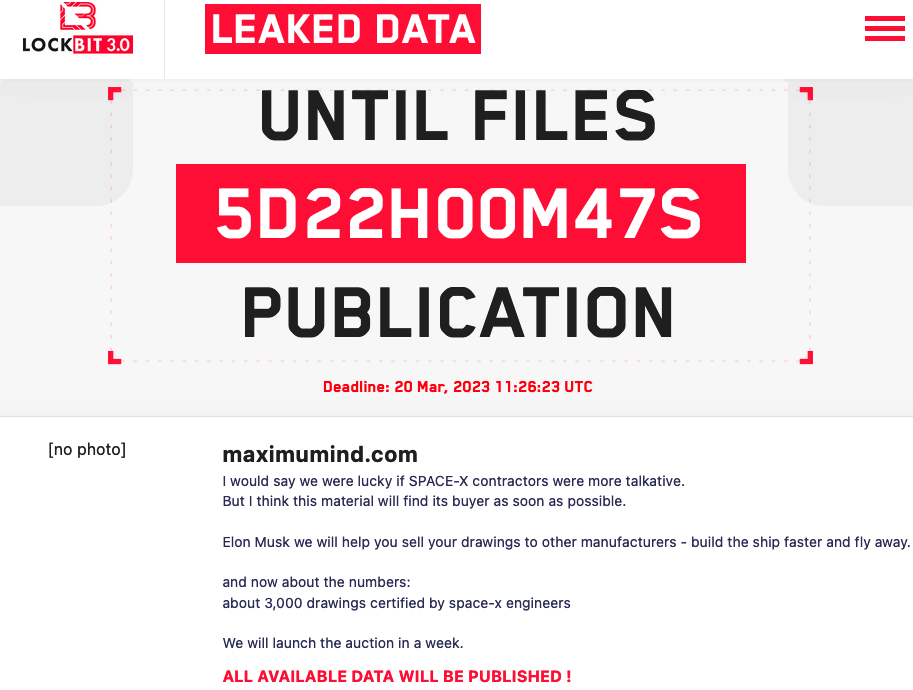
SpaceX ransomware

SecurityWeek has reached out to both SpaceX and Maximum Industries for comment, but none of them have responded. 

While Maximum Industries may have been hacked, it’s not uncommon for cybercrime groups to make exaggerated claims regarding the impact of their attacks or the value of the data they have obtained. 

The LockBit ransomware operation was launched in 2019 and it has been evolving ever since. The cybercriminals, believed to be operating out of Russia, exploit unpatched vulnerabilities, rely on insiders, or acquire access from specialized groups to gain access to victim systems. Once they have access, they collect valuable data, after which they deploy file-encrypting malware. 

For more than a year now, LockBit has been the most active ransomware operation. To date it has targeted well over 1,000 organizations, including major companies such as German car parts giant Continental.

Advertisement. Scroll to continue reading.

Related: New ‘Exfiltrator-22’ Post-Exploitation Framework Linked to Former LockBit Affiliates

Related: Russian National Arrested in Canada Over LockBit Ransomware Attacks

Related: LockBit Ransomware Site Hit by DDoS Attack as Hackers Start Leaking Entrust Data

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Trending

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Join as speakers examine the various components of ASM strategy, the push to mandate continuous asset visibility and inventory tools, and the use of red-teaming, bug bounties and pen-tests in modern security programs.

Register

Explore what it takes to operationalize continuous authorization at scale, including the technical, organizational, and cultural changes required.

Register

People on the Move

Veritas Capital has appointed Joel Fulton as Chief Information Security Officer.

incident.io has appointed Carlos Gonzalez-Cadenas as Chief Operating Officer.

Ruben D. Chacon has joined ADM as Vice President and Global CISO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





