
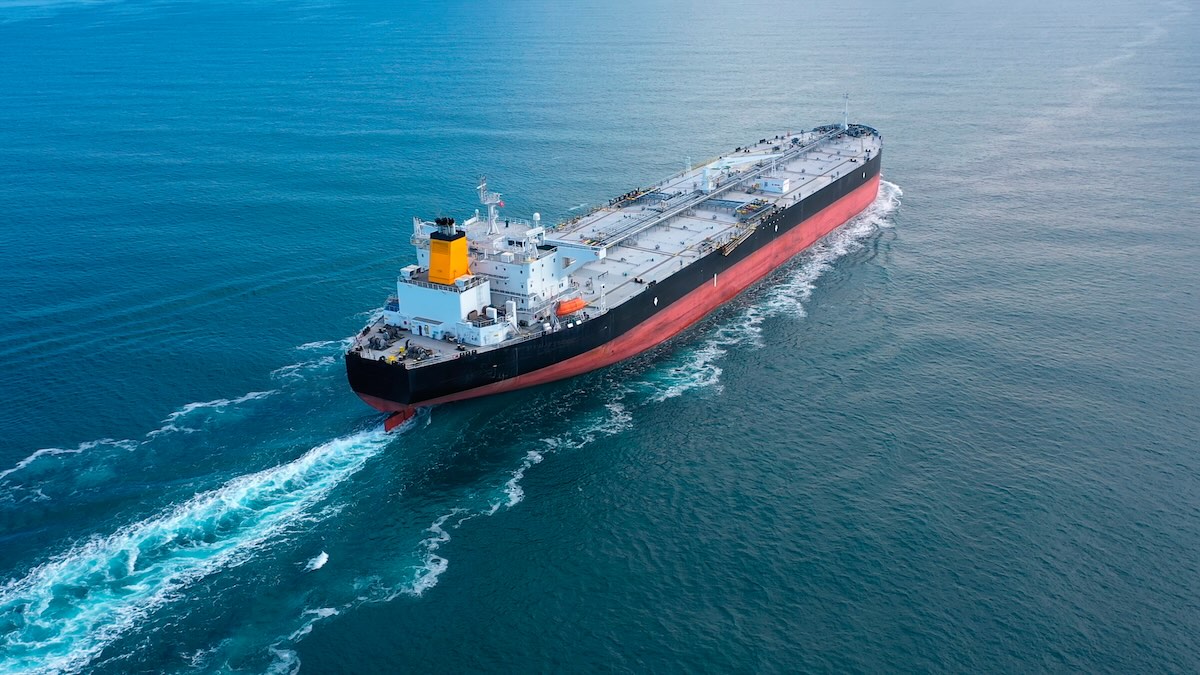
Two oil tankers bound for Texas were boarded by US Coast Guard and FBI personnel last month after cyberattacks disrupted the vessels during their voyage toward the United States, according to a CBS News report citing US officials.
One of the ships, the VL Prosperity, is a Liberian-flagged crude tanker that left Egypt on August 1 en route to Galveston, Texas, per vessel-tracking records cited by CBS News.
Iran’s Mehr News Agency reported on August 20 that the cyberattack had allegedly occurred on August 7 as the tanker passed through the Strait of Gibraltar. Citing a crew member, the Iranian outlet said the intrusion reached the engine room, with hackers slowing coolant flow, raising engine speed and interfering with fuel delivery.
Hands-On Cyber-Physical Systems Training at ICS Cybersecurity Conference
The hackers also allegedly accessed navigation and cargo systems and cut off the ship’s communications for roughly 30 hours.
One day after Mehr’s report, a team that included Coast Guard cyber specialists, law enforcement, a vessel inspector, and FBI Cyber Action Team members boarded the VL Prosperity and spent four days aboard.
The Wall Street Journal reported that the second ship was boarded on August 24. Both vessels were boarded after they arrived in the Gulf of Mexico.
The Coast Guard has not publicly linked the incident to Iran. Rear Adm. Amy Grable, commander of Coast Guard Cyber Command, told CBS News that investigators did find evidence of a malicious cyber actor after reviewing the vessel’s IT and other onboard systems.
She noted that nothing uncovered during the inspection suggested the tanker was unsafe to operate. This was one of an estimated 40-50 similar boardings the Coast Guard’s Cyber Protection Team has carried out over the past year, Grable said.
Quinton DuBose, a former Coast Guard cyber official, pushed back on the idea that hackers could seize full command of a supertanker, arguing the more realistic risk is an attacker degrading enough individual systems to make safe operation difficult.
Investigators are still working to determine whether the two tanker incidents are connected and whether Iran or another state actor is responsible. DuBose urged caution around the Iranian coverage, noting that Iran-linked actors have a history of overstating their cyber capabilities.
Cyber threats to the maritime sector
The incident comes just days after the US Coast Guard announced a dedicated Office of Maritime Cybersecurity Policy, which will serve as its central authority for developing and implementing policies governing the cyber safety and security of the marine transportation system.
The cybersecurity community has long warned that the maritime sector’s reliance on aging, unmanaged OT systems, satellite communications, and connected IoT devices leaves both vessels and ports dangerously exposed to cyberattack.
Attackers can exploit WiFi, HF radio, and SATCOM links — or simply an infected USB stick — to gain access, with successful compromise potentially granting remote control over a ship’s throttle, rudder, or navigation systems.
Beyond ransomware, which has already disrupted shipping operations, experts point to even more severe scenarios such as GPS spoofing, AIS manipulation to disguise a vessel’s true location, or deliberately running a ship aground to block a critical waterway.
Given that roughly 80% of global goods move by sea, a targeted attack could trigger billions of dollars in losses and cascading supply shortages.
Related: Ransomware Attacks on Manufacturers Surge as Supply Chain Risk Grows
Related: US, UK, Dutch Agencies Expose Iranian ‘Chosen Brick’ Surveillance Malware
Related: White House Mobilizes Security Firms for Operations Against Foreign Cybercrime Gangs






