CONFERENCE CISO Forum Virtual Summit 2026 - View all Sessions
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Latest Cybersecurity News

Federal officials have yet to say what caused the communications disruption or whether they are investigating a possible cyberattack.
Noteworthy stories that might have slipped under the radar: Siemens details security advisory policy, OpenAI Codex backdoor risk, Microsoft warns of model weight backdoors.

Microsoft is trying different ways to identify the cause of the problem and get its servers back online, using “a measured approach to identify and repair affected infrastructure.”

The web scraping company says an intruder accessed customer accounts and obtained personal information or stored data.

Enea says SilentAir hijacked mobile network nodes to intercept calls and messages, with Taiwanese subscribers the primary targets.

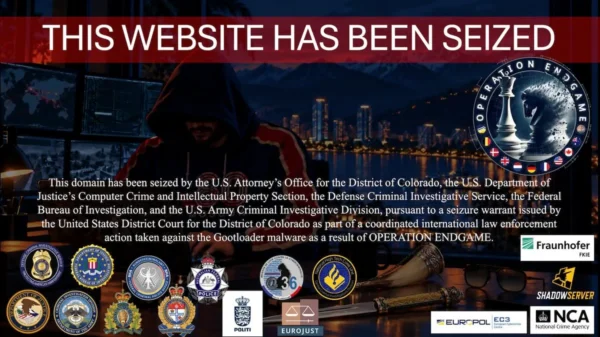
Investigators seized 235 servers and 257 domains, along with 6.4 million victim credentials as part of Operation Endgame.

Successful exploitation could lead to unexpected behavior or denial-of-service (DoS) conditions.

Daybreak Red Team pentests web applications with AI agents, while Defense Factory investigates security findings and prepares patches.

It abuses CLFS and Windows Defender to trigger arbitrary file creation in the context of the antimalware process.

PHP2Shell enabled initial compromise, while CVE-2026-123039 allowed attackers to elevate privileges to root.

Dubbed 4EverAble2Shell, the flaw could allow remote, unauthenticated attackers to execute code with root privileges.

Also Thursday, the FBI blamed North Korea for a separate social engineering scheme that officials say resulted in the theft of $400 million worth of cryptocurrency.

Microsoft says failed server health checks disrupted Outlook and other Microsoft 365 services. The company is still investigating the cause and has disclosed no evidence of a cyberattack.

FAA Ground stop FAA Ground stop

Federal officials have yet to say what caused the communications disruption or whether they are investigating a possible cyberattack.

Nightmare Eclipse Nightmare Eclipse

It abuses CLFS and Windows Defender to trigger arbitrary file creation in the context of the antimalware process.

Check Point Check Point

PHP2Shell enabled initial compromise, while CVE-2026-123039 allowed attackers to elevate privileges to root.

Top Cybersecurity Headlines

Dubbed 4EverAble2Shell, the flaw could allow remote, unauthenticated attackers to execute code with root privileges.

The mod_http2 race condition, CVE-2026-119618, could let unauthenticated attackers execute code on servers with HTTP/2 enabled.

The malicious activity started shortly after a researcher dropped over 30 zero-days. N-able patched the unauthenticated ones.

SecurityWeek Industry Experts

More Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers’ agents write to running a coordinated system of security agents you’ve built yourself.

Register


Upcoming Cybersecurity Events

CISO Forum Virtual Summit

The 2026 Virtual CISO Forum brings together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.
[November 10 & 11, 2026 | Virtual]

Read More
CISO Forum 2026 Year-End Review Virtual Roundtable

SecurityWeek’s CISO Forum 2026 Year-End Virtual Roundtable will reflect on a landmark year in security and discuss how to fortify your enterprise strategy for 2027.
[December 2, 2026 | Virtual]

Read More
Cyber AI and Automation Summit 2026

SecurityWeek’s Cyber AI & Automation Summit pushes the boundaries of security discussions by exploring the implications and applications of predictive AI, machine learning, and automation in modern cybersecurity programs.
[December 8 & 9, 2026 | Virtual]

Read More
Zero Trust Summit Now On-Demand

SecurityWeek’s 2026 Zero Trust Summit will deep-dive into the world of digital identity management and the role of zero-trust principles and associated technologies
[Originally October 14, 2026]

Read More

Vulnerabilities

Cybercrime

On Wednesday June 13, in the run-up to Mexico's July 1 presidential election, a website operated by the rightist National Action Party (PAN) was taken off-line for several hours by a DDoS attack. The outage occurred at the time of a televised presidential debate, and just following a point at which the PAN candidate held up a placard with the website address claiming it held proof of potential corruption.

London, UK-based start-up Tessian has raised $13 million in a Series A funding round led by Balderton Capital. Existing investors Accel, Amadeus Capital Partners, Crane, LocalGlobe, Winton Ventures and Walking Ventures also participated. It brings Tessian's total funding, including initial Angel investments and seed funding, to $16.8 million.

Finland-based F-Secure announced on Monday that it has entered an agreement to acquire cybersecurity consultancy MWR InfoSecurity for over €91.6 million ($106 million) in cash and the promise of a significant earn-out if business objectives are achieved until the end of 2019.

The number of cyber-attacks targeting Singapore skyrocketed from June 11 to June 12, during the meeting between U.S. President Donald Trump and North Korean President Kim Jong-un in a Singapore hotel, and most of these attacks originated from Russia, F5 Labs reports.

Bengaluru, India-based security services and products firm Network Intelligence Inc (NII) has raised Rs 33-crore funding (approximately $4.8 million) from private equity firm Helix Investments. The money will be used for product development and to expand operations in the U.S. and Europe. The investment values the firm at $22.7 million.

A newly discovered attack relying on malicious Word documents and PowerShell scripts appears related to the MuddyWater cyber-espionage campaign, Trend Micro reports.

Europol announced this week that several French nationals were arrested in the past year on suspicion of being involved with Rex Mundi, a group that hacked into the systems of several organizations and attempted to blackmail them.

Event image poster

The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.

Learn More

Application Security

Application Security

Using thousands of hijacked accounts, the wfx-loot campaign planted a CI secret stealer that ran in over 1,800 GitHub repositories.

Cloud Security

Cloud Security

Created by Zerto and Kashya veterans, the startup has launched a platform designed to recover whole cloud applications. 

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.