
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Cybercrime

Google Spots Attacks Exploiting iOS Zero-Day Flaws

Google security researchers revealed that two of the vulnerabilities patched by Apple on Thursday with the release of iOS 12.1.4 were zero-day flaws exploited in the wild by malicious actors.

Google security researchers revealed that two of the vulnerabilities patched by Apple on Thursday with the release of iOS 12.1.4 were zero-day flaws exploited in the wild by malicious actors.

iOS 12.1.4 resolves a total of four vulnerabilities. Two are related to the recently discovered FaceTime spying bug, and the other two are memory corruption issues that allow a malicious application to elevate privileges and execute arbitrary code.

One of the flaws, tracked as CVE-2019-7286, impacts the Foundation component in iOS and it allows a malicious application to gain elevated privileges. The second vulnerability, identified as CVE-2019-7287, impacts IOKit and it can be exploited by a malicious app to execute arbitrary code with kernel privileges.

Apple has credited Clement Lecigne of Google Threat Analysis Group, along with Ian Beer and Samuel Groß of Google Project Zero for reporting these issues. An anonymous researcher has also been credited by the tech giant.

Project Zero Team Lead Ben Hawkes revealed on Twitter that both CVE-2019-7286 and CVE-2019-7287 have been exploited in the wild, but no details have been shared about the vulnerabilities or the attacks.
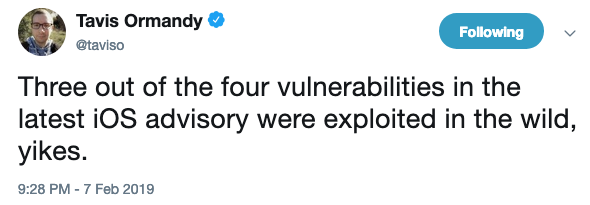
Tweet from Google Project Zero researcher Tavis Ormandy

It’s worth noting that CVE-2019-7286 has also been patched in macOS Mojave with the release of a supplemental update for version 10.14.3, which also resolves the Facetime-related issues.

Advertisement. Scroll to continue reading.

While it may seem that iOS and macOS vulnerabilities are rarely exploited in attacks, some experts warn that it’s actually not that uncommon.
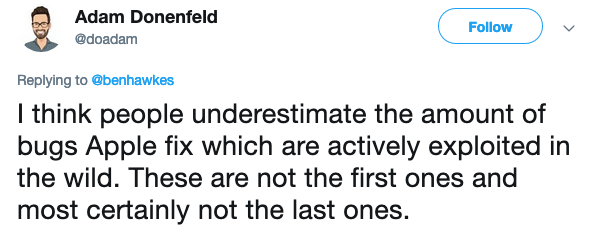
Zimperium's Adam Donenfeld warns of attacks exploiting Apple flaws

Apple has also released an update for Shortcuts for iOS to address a local information disclosure flaw and a sandbox bypass issue.

Related: Apple Patches Dozens of Vulnerabilities in iOS, macOS

Related: Apple Patches Tens of Flaws in iOS, macOS, Safari

Related: iOS 12 Brings Patches for 16 Security Vulnerabilities

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Cohere has appointed Jaya Baloo as CISO.

Jensen Huang has resigned as President and Chief Executive Officer at NVIDIA.

Sean Sweeney has become CIO of the City of Charleston, South Carolina.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





