
Nine vulnerabilities, including potentially serious flaws, were patched recently in a couple of electric power management products made by Schweitzer Engineering Laboratories (SEL).
SEL is a US-based company that provides a wide range of products and services for the electric power sector, including control systems, generator and transmission protection, and distribution automation.
Researchers at industrial cybersecurity firm Nozomi Networks have analyzed the company’s SEL-5030 acSELerator QuickSet and SEL-5037 Grid Configurator, software products designed to allow engineers and technicians to configure and manage devices for power system protection, control, metering and monitoring, and to create and deploy settings for SEL power system devices.
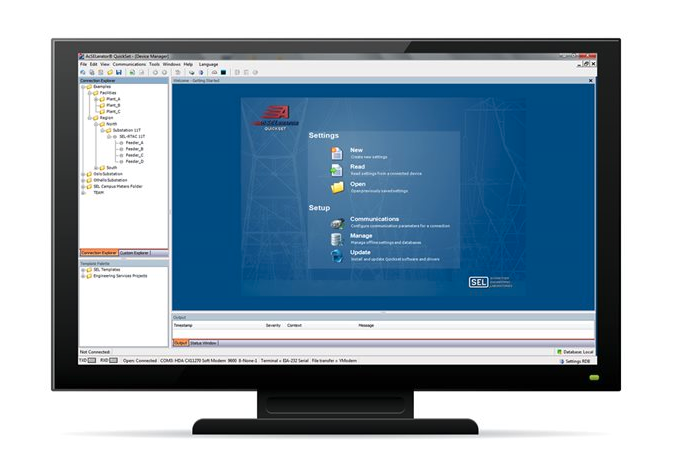
Nozomi researchers discovered a total of nine vulnerabilities, including four that have been assigned a ‘high severity’ rating — the remaining five are ‘medium severity’.
The most severe, according to Nozomi, is CVE-2023-31171, which allows arbitrary code execution on the engineering workstation running the SEL software by getting the targeted user to import a device configuration from a specially crafted file. The flaw can be chained with CVE-2023-31175, which allows an attacker to escalate privileges.
A malicious insider or an external threat actor (via social engineering) could exploit the vulnerabilities to steal sensitive data, for surveillance or manipulation of the device’s logic, and for lateral movement inside the victim’s network.
Another serious issue can allow arbitrary command execution and changing a device’s configuration, either by getting the targeted user to click on a link, or by setting up a watering hole that the victim is likely to visit.
“The native functionality to clear the terminal history could allow an attacker to cover up and erase their activities, making it more difficult for a target victim to spot any suspicious activity that may have happened in the background on their systems,” Nozomi warned.
SEL has been notified and it has released software updates that should patch these vulnerabilities.
This is not the first time Nozomi has found vulnerabilities in SEL products. In May, the company reported identifying 19 security holes in SEL computing platforms running the vendor’s Realtime Automation Controller (RTAC) suite.
“Worst case scenario, by chaining some of these vulnerabilities and performing a multi-step attack, an unauthenticated remote attacker could alter the core functionality of the device, allowing them to tamper with the information shown to operators or the configuration of the device itself,” Nozomi said at the time. “Additionally, access to all other systems protected by the same credentials could be acquired, allowing them to easily move laterally in the power infrastructure.”
Learn More at SecurityWeek’s ICS Cyber Security Conference
The leading global conference series for Operations, Control Systems and OT/IT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
October 23-26, 2023 | Atlanta
www.icscybersecurityconference.com
Related: Power Management Product Flaws Can Expose Data Centers to Damaging Attacks, Spying
Related: Power Grid Protection Firm SEL Patches Severe Software Flaws
Related: Exploited Solar Power Product Vulnerability Could Expose Energy Organizations to Attacks
Related: Australian Energy Software Firm Energy One Hit by Cyberattack






