Two months after taking down the Alphv/BlackCat ransomware operation, the US announced a $10 million reward for information on the cybergang’s key members.
Operating since late 2021 under the ransomware-as-a-service business model, BlackCat has made over 1,000 victims worldwide, including organizations such as MGM Resorts, NCR, Reddit, Swissport, and Western Digital.
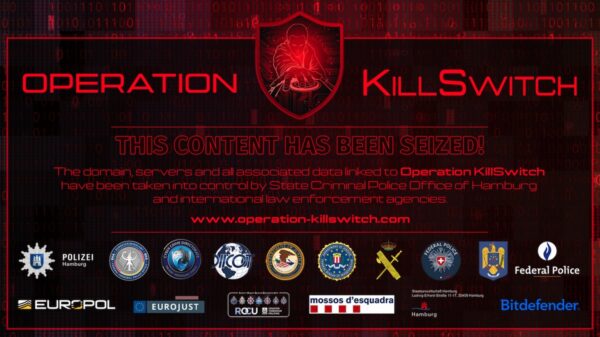
In early December 2023, the group’s Tor-based website went offline following a presumed law enforcement takedown that was officially confirmed roughly two weeks later, when the FBI also released a free decryption tool for the ransomware’s victims.
The takedown was possible after the FBI obtained credentials providing access to the panels the group’s members were using for communication.
In response, the cybergang briefly “unseized” its domain and announced lifting all restrictions imposed on affiliates, allowing them to target any type of organization in any country.
The group also claimed that the decryption tool was only good for roughly 400 organizations, but that more than 3,000 other victims would never recover their data.
According to the FBI, the decryption tool has helped dozens of victims restore their systems, saving them from paying up approximately $99 million in ransom demands.
Now, the US is offering a reward of up to $10 million for information that would help law enforcement identify or locate the BlackCat group leaders, and up to $5 million for information leading to the arrest or conviction of any group affiliate.
The US has set up a tip line that can be accessed using the Tor browser, and encourages interested parties to provide information using that portal, via local FBI offices, or via US embassies.
Last week, the US announced a $10 million reward for information on the leaders of the Hive ransomware, which was disrupted in January 2023.
Related: Ransomware Attack Knocks 100 Romanian Hospitals Offline
Related: Ransomware Payments Surpassed $1 Billion in 2023: Analysis