
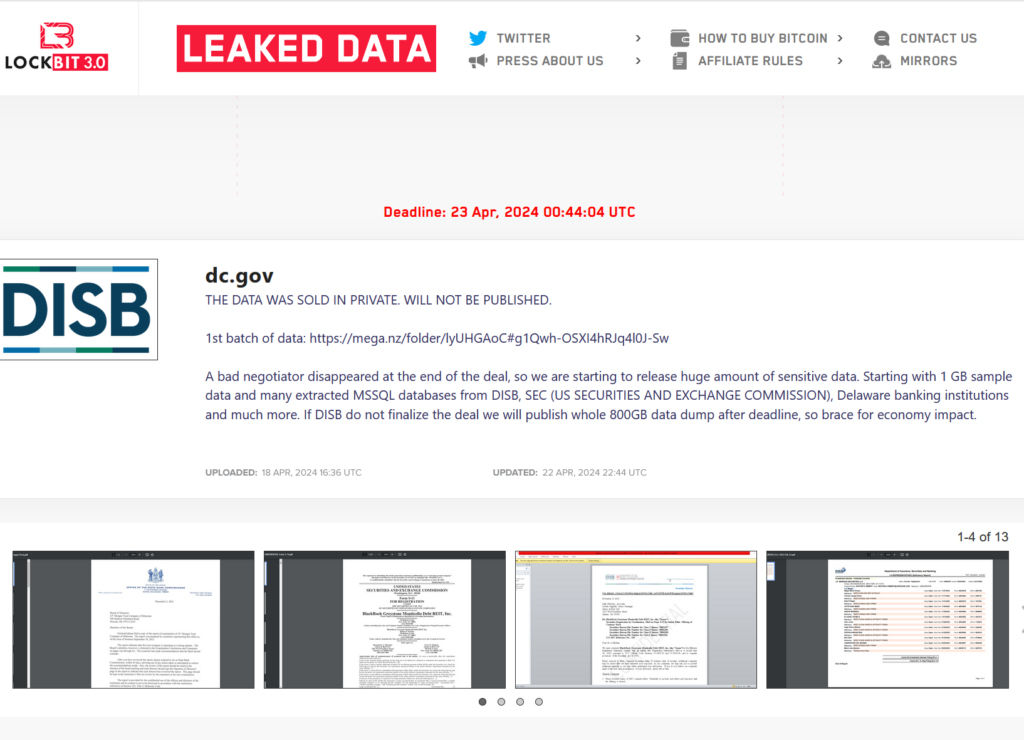
The LockBit ransomware gang has leaked 1Gb of data allegedly stolen from the District of Columbia’s Department of Insurance, Securities and Banking (DISB).
The group claims to be in the possession of 800Gb of data pertaining to DISB, the US Securities and Exchange Commission (SEC), Delaware banking institutions, and other financial entities, and threatens to release it unless DISB pays a ransom.
The data appears to have been stolen from DISB’s STAR system client in late March, during a cyberattack on Tyler Technologies, a software and services provider for the public sector.
In separate incident notices, Tyler and DISB revealed that the attack involved unauthorized access to a cloud environment hosting DISB’s STAR system client data.
The system was immediately taken offline and, while file-encrypting ransomware was deployed on the compromised system, Tyler has been working on restoring the environment and associated data using available backups.
In an April 19 update, Tyler confirmed that information allegedly stolen from the STAR system was leaked online, but said it has yet to determine the full scope of the data breach.
Potentially compromised information, the contractor said, may include names, dates of birth, Social Security numbers, driver’s license numbers, and other information.
“We have confirmed evidence that the threat actor acquired information from the system. We are working with third-party cybersecurity forensic experts to identify the full impact. As of April 18, the threat actor published information they claim was acquired from the STAR system,” the company said.
Tyler also noted that it has yet to identify individuals whose personally identifiable information (PII) might have been stolen in the attack and that it would start notifying them once the identification process is completed.
The attack, Tyler pointed out, was unrelated to a 2020 ransomware attack that impacted its internal corporate network and phone systems and forced it to shut down various systems, including its website.
The Texas-based Tyler Technologies provides property tax lifecycle management solutions, civic services solutions, a secure system for accessing official records, regulatory solutions, and integrated corrections, case management, and public safety solutions.
Related: Cannes Hospital Cancels Medical Procedures Following Cyberattack
Related: Watch Now: Ransomware Resilience & Recovery Summit Sessions Now on Demand
Related: LockBit Ransomware Gang Resurfaces With New Leak Site






