
Just as the U.S. had been preparing to accuse Russia of launching cyberattacks against its energy and other critical infrastructure sectors, the notorious Russia-linked threat group known as Sofacy was spotted targeting a government agency in Europe.
The United States on Thursday announced sanctions against Russian spy agencies and more than a dozen individuals for trying to influence the 2016 presidential election and launching cyberattacks, including the destructive NotPetya campaign and operations targeting energy firms.
The Department of Homeland Security and Federal Bureau of Investigation issued a joint technical alert via US-CERT last year to warn about attacks launched by a group known as Dragonfly, Crouching Yeti and Energetic Bear on critical infrastructure. Researchers previously linked Dragonfly to the Russian government and now the DHS has officially stated the same.
US-CERT has updated its alert with some additional information. The new version of the alert replaces “APT actors” with “Russian government cyber actors.” The DHS said that based on its analysis of malware and indicators of compromise, Dragonfly attacks are ongoing, with threat actors “actively pursuing their ultimate objectives over a long-term campaign.”
This is not the first time the U.S. has imposed sanctions on Russia over its attempt to influence elections. Russia has also been accused by Washington and others of launching the NotPetya attack last year. The Kremlin has always denied the accusations, but President Vladimir Putin did admit at one point that patriotic hackers could be behind the attacks.
If Dragonfly and Sofacy (aka Fancy Bear, APT28, Sednit, Tsar Team and Pawn Storm) are truly operating out of Russia, they don’t seem to be discouraged by sanctions and accusations.
On March 12 and March 14, security firm Palo Alto Networks spotted attacks launched by Sofacy against an unnamed European government agency using an updated variant of a known tool.
Sofacy has been using a Flash Player exploit platform dubbed DealersChoice since at least 2016 and it has continued improving it. The latest version has been delivered to a government organization in Europe using a spear phishing email referencing the “Underwater Defence & Security” conference, which will take place in the U.K. later this month.
What makes the new version of DealersChoice interesting, according to Palo Alto Networks, is the fact that it employs a clever evasion technique that has not been seen in the past.
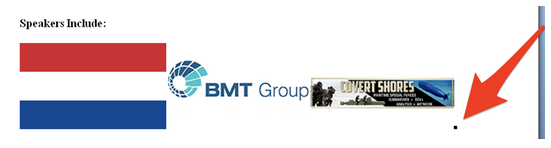
Older versions of DealersChoice loaded a malicious Flash object as soon as the bait document was opened. The latest samples, however, include the Flash object on page three of the document and it’s only loaded if users scroll down to it. This Flash object, displayed in the document as a tiny black box, contacts the command and control (C&C) server to download an additional Flash object that contains the actual exploit.
Kaspersky reported last week that it had seen overlaps between attacks launched by Sofacy and campaigns conducted by other state-sponsored cyberspies, including ones linked to China and the United States.







You must be logged in to post a comment Login