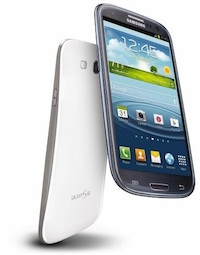
The security vulnerability that could fully wipe Samsung Galaxy S III device appears to not be limited to just Samsung devices after all, but affects most smartphones running older versions of Android.
 Ravi Borgaonkar, a researcher from Germany’s Technical University Berlin, demonstrated how he could fully wipe a Samsung Galaxy S III smartphone just by clicking on a single HTML link at the Ekoparty security conference in Argentina last week. The USSD code to execute the wipe command could be embedded in a link or QR code, or sent to the device over a near-frequency-communications connection, Borgaonkar said. Just by clicking on the link in an email, Website, and even on social networks such as Twitter, was enough to trigger the command.
The vulnerability originally appeared to be linked to the way the TouchWiz dialer software on Samsung devices handles USSD codes and how the stock Web browser handles the “tel:” protocol, Borgaonkar said in his presentation. Additional testing showed that some Samsung Galaxy Tab devices were affected, Borgaonkar said on Twitter. Samsung said the issue in Galaxy S III had already been fixed through a software update and encouraged users to use the Over-the-Air capability to download the fix.
Related: Creating Android Malware Is Trivial With Available Tools
“We would like to assure our customers that the recent security issue concerning the GALAXY S III has already been resolved through a software update,” Samsung said in a statement.
While Borgaonkar’s presentation focused on Samsung Galaxy S III phones, he said on Twitter that the vulnerability was not limited to Samsung devices but affected a wider pool of Android devices. Mobile researcher Dylan Reeve verified the problem existed on an HTC One X running HTC Sense 4.0 on Android 4.0.3 (Ice Cream Sandwich) and a Motorola Defy running Cyanogen Mod 7 on Android 2.3.5 (Gingerbread).
The flaw appeared to originate in older versions of Google’s Android operating system, according to tests run by the Android Police blog. In fact, the vulnerability wasn’t in TouchWiz but in the standard Android dialer. While the vulnerability was fixed in the Android OS three months ago, many devices remained vulnerable because device manufacturers did not patch the flaw on their custom versions of Android and carriers did not push out a fix to their customers.
Reeve created a Web page that checks whether the Android device is vulnerable to the USSD flaw. If clicking on the test site from an Android device causes the device to display its IMEI code, then it is vulnerable. Borgaonkar also has a testing site.
There were reports that clicking on the link while using the Chrome Web browser doesn’t cause the remote wipe, suggesting the issue is limited to the stock browser on affected devices. There were other reports claiming Chrome or other browsers didn’t make a difference. Devices running JellyBean (Android 4.1) were not affected because the stock dialer had been patched.
The easiest way to mitigate the risk if the user can’t update the operating system (due to carrier restrictions, for example), is to install another dialer, Reeve said. There are several options available on Google Play.
Related Reading: Galaxy S3 Hacked Via NFC During Mobile Pwn2Own
Related Reading: Mobile Industry Slow to Push Android Updates to Users
Related Reading: Creating Android Malware Is Trivial With Available Tools