
Moxa Urges Users to Replace Discontinued Industrial AP Filled With Security Holes
More than a dozen serious vulnerabilities have been found in an industrial wireless access point (AP) made by Taiwan-based industrial networking and automation solutions provider Moxa, but the vendor only addressed the flaws several months after exploits were made public.
Researcher Samuel Huntley discovered in early 2018 that Moxa’s AWK-3121 series industrial AP/bridge/client product was affected by a total of 14 vulnerabilities.
Moxa and the DHS’s Cybersecurity and Infrastructure Security Agency (CISA) this week published advisories describing the vulnerabilities found by Huntley. CISA says the impacted product is used worldwide in the critical manufacturing, energy, and water and wastewater systems sectors.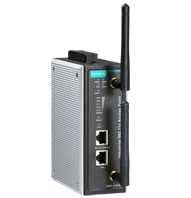
Huntley told SecurityWeek that he reported his findings to Moxa, but he did not receive any response from the company. In early June 2019, he decided to publicly disclose his findings, including proof-of-concept (PoC) exploits. Following his disclosure, CISA reached out to him and made contact with Moxa in an effort to get the company to address the flaws.
In the security advisory it published on December 2, Moxa informed customers about the existence of the vulnerabilities, but told them that the AWK-3121 series AP has been phased out and replaced with the AWK-1131A series.
The researcher believes the product was still in service at the time when he initially discovered the vulnerabilities.
Learn More About Flaws in Industrial Products at SecurityWeek’s 2020 ICS Cyber Security Conference
Most of the 14 vulnerabilities have been assigned severity ratings of critical and high. The more serious of the flaws can be exploited to gain access to sensitive system log information without authentication, execute arbitrary commands on the device, and inject a malicious payload via an XSS attack.
Some of the other flaws are related to the failure to protect sensitive information against man-in-the-middle (MitM) attacks, and one XSS vulnerability could allow an attacker to obtain session cookies that they could use to log into the AP.
Huntley told SecurityWeek that while most of the vulnerabilities are not directly exploitable from the internet, an attacker could leverage a cross-site request forgery (CSRF) flaw that he has found to execute attacks remotely. CSRF attacks involve tricking an administrator into visiting a specially crafted website that is set up to serve exploits.
SecurityWeek has reached out to Moxa to find out why it took them so long to release an advisory, but the company has yet to respond.
The poor handling of vulnerability disclosures by industrial automation vendors is not uncommon. It was revealed recently that ABB addressed a critical vulnerability in a plant historian product five years after the company learned of its existence from a researcher.
Related: Many Vulnerabilities Discovered in Moxa Industrial Switches
Related: Cisco Finds Many Flaws in Moxa Industrial APs
Related: Hardcoded Credentials Give Attackers Full Access to Moxa APs







You must be logged in to post a comment Login