
Microsoft Releases Enhanced Mitigation Experience Toolkit (EMET) 2.0
Announced at the Black Hat 2010 conference in July, Microsoft’s updated Enhanced Mitigation Experience Toolkit (EMET) 2.0 has been released and is now available for download.
EMET is specifically designed to block targeted attacks against unfixed vulnerabilities. The toolkit is free and helps improve the security of applications without having to recode them. Developers and IT security professionals are able to add new and existing security mitigation technologies to software in order to help protect against exploitation of vulnerabilities. All mitigations can be applied on a per-application basis with customized settings, allowing developers to bring newer security mitigations to older applications.
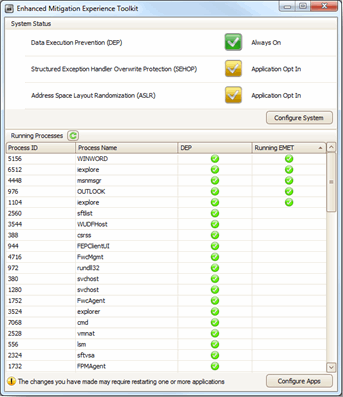
EMET 2.0 allows users to both configure the system policy for mitigations as well as to configure mitigations on a per executable basis. The first option allows the user to set the defaults for system supported mitigations; for instance choosing whether one should be enabled for all processes, enabled for only those that chose to opt in, disabled entirely etc.
The tool supports both 32- and 64-bit applications and has been updated with a new unified graphical user interface that shows running processes and whether EMET is currently active for them. Two new mitigations have been added — mandatory ASLR and EAT address filtering. Version 2.0 now includes support for viewing and setting systemwide mitigation settings.
It adds the following mitigations to applications that do not support them natively:
• Structured Error Handling Overwrite Protection (SEHOP) prevents Structured Exception Handling (SEH) overwrite exploitation by performing SEH chain validation.
• Dynamic Data Execution Prevention marks portions of a process’s memory non-executable, making it difficult to exploit memory corruption vulnerabilities.
• NULL page allocation allocates the first page of memory before program initialization and blocks attackers from taking advantage of NULL references in user mode.
• Heap Spray Allocation pre-allocates memory addresses to block common attacks that fill a process’s heap with specially crafted content.
• New in EMET 2.0 is mandatory address space layout randomization (ASLR), as well as non-ASLR-aware modules on Windows Vista, Windows Server 2008 and Windows 7.
• Also new in EMET 2.0, export address table (EAT) uses hardware breakpoints to filter access to the EAT of kernel32.dll and ntdll.dll, blocks access if the instruction pointer is not inside a module, and breaks current common metasploit shellcodes.
Microsoft warns that some security mitigation technologies may break applications and reminds users that it’s important to thoroughly test EMET in all target use scenarios before rolling it out to a production environment.
You can download EMET 2.0 here.







You must be logged in to post a comment Login