

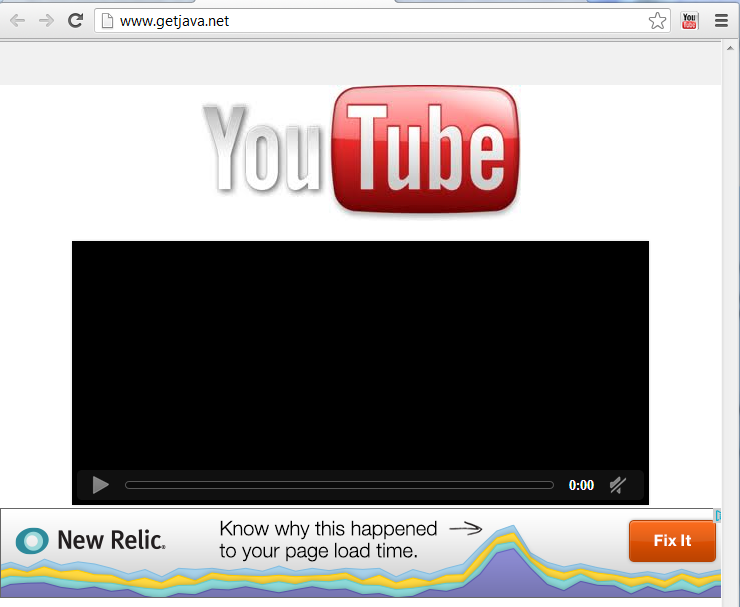
Researchers at Zscaler have discovered a fake YouTube page that is hosting malicious Chrome extensions. Such pages, as seen in the past, prey on the uninformed users with poorly patched systems to spread malware.
Fake YouTube pages have been leveraged by criminals for years, and often used to spread malware under the guise of video codecs. Normally, they target Internet Explorer and Firefox users.
Zscaler’s discovery of such a page targeting Google Chrome users is new. The fact that the malicious Chrome extension is hosted on the official Google Chrome store is bold, but the attacker behind this latest scheme slaps the search giant a second time by leveraging the Google URL shortening service to propagate the attack.
“It looks like the author of this malicious extension doesn’t have a high opinion of Google’s security by using Google for hosting the extension and using their URL shortener to inject the malicious JavaScript,” Zscaler’s Julien Sobrier wrote in the company’s blog.
Assuming the victim clicks on any of the adds, or the video player itself, the fake page attempts to install a Chrome extension that claims to record YouTube videos. The extension warns the user that the permissions essentially hand over complete control, but like other warnings – the attacker is counting on the fact that this heads-up will be ignored.
Once installed, the ability to access Tools or Settings in Chrome is denied, and the victim’s (when the attack was fully functional) accounts on Facebook, YouTube, Last.fm, and Twitter are spammed with additional malicious links.
The attack is somewhat disabled, but parts of it are working – including the spamming of Facebook’s Timeline. It’s possible that the other three services can be targeted down the line, as the attacker needs only to acquire additional hosting.
Zscaler has more details available on their blog. It’s likely that the malicious extension was cleared for hosting on the official store, due to the fact that it complies by offering a control warning. In June 2012, Google disabled the installation of extensions for 3rd-party sites, and silent installs were given the axe later that same year.






