
Syrian-linked hackers recently switched to COVID-19-themed lures as part of a long-running surveillance campaign, Lookout security researchers reveal.

Hi, what are you looking for?

Syrian-linked hackers recently switched to COVID-19-themed lures as part of a long-running surveillance campaign, Lookout security researchers reveal.
Swiss-based global shipping giant Mediterranean Shipping Company (MSC) has confirmed that a recent outage was caused by a malware attack that affected its headquarters in Geneva.
Linksys has prompted users to reset passwords after learning that hackers were leveraging stolen credentials to change router settings and direct customers to malware.
SAP this week released its latest set of security patches, which brings a total of 23 Security Notes, including five that address Hot News vulnerabilities.
TPG Capital-backed Digital.ai launched on Wednesday with a new software development and security platform. The new company, based in Plano, Texas, is a combination of CollabNet VersionOne, XebiaLabs, and Arxan Technologies.
Threat actors working for North Korea have also been hired by others to hack websites and extort targets, the U.S. government says in a new cyber alert.
SafeBreach has raised a further $19 million to improve and expand its breach-and-attack simulation platform, which allows customers to assess their security posture against a continuous barrage of genuine, but safe, hacker behaviors.
Metasploit Team Unveils Community Powered Knowledge Base of Vulnerabilities and Insights
Five Ways to Steer Your Security Organization in a Toxic Environment
The recently disclosed attack aimed at two websites pertaining to the San Francisco International Airport (SFO) is the work of Russian hackers, ESET claims.
Awake Security, a California-based company that specializes in network traffic analysis, has raised $36 million in a Series C funding round.
Oracle this week released its April 2020 collection of security patches, which includes a total of 397 fixes for vulnerabilities affecting two dozen products.The software giant also revealed that 264 of the addressed vulnerabilities could be exploited remotely without authentication.
A report published this week by the U.S. Government Accountability Office (GAO) shows that the Pentagon’s cyber hygiene initiatives have not been completed and in some cases no one is keeping track of their progress.
Identity verification and authentication provider Onfido today announced the closing of a $100 million funding round that brings the total raised by the company to date to $200 million.
HackerOne announced on Tuesday that the bug bounty program of Chinese technology giant Tencent is now accessible through its platform.
Microsoft’s Update Tuesday patches for April 2020 address 113 vulnerabilities, including three Windows flaws that have been exploited in attacks for arbitrary code execution and privilege escalation.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Join SecurityWeek today for a virtual summit exploring the strategies and tools organizations need to discover, prioritize, and defend their expanding attack surfaces.
Microsoft fixed vulnerabilities across Azure and AI-branded products, with privilege escalation flaws accounting for the majority.

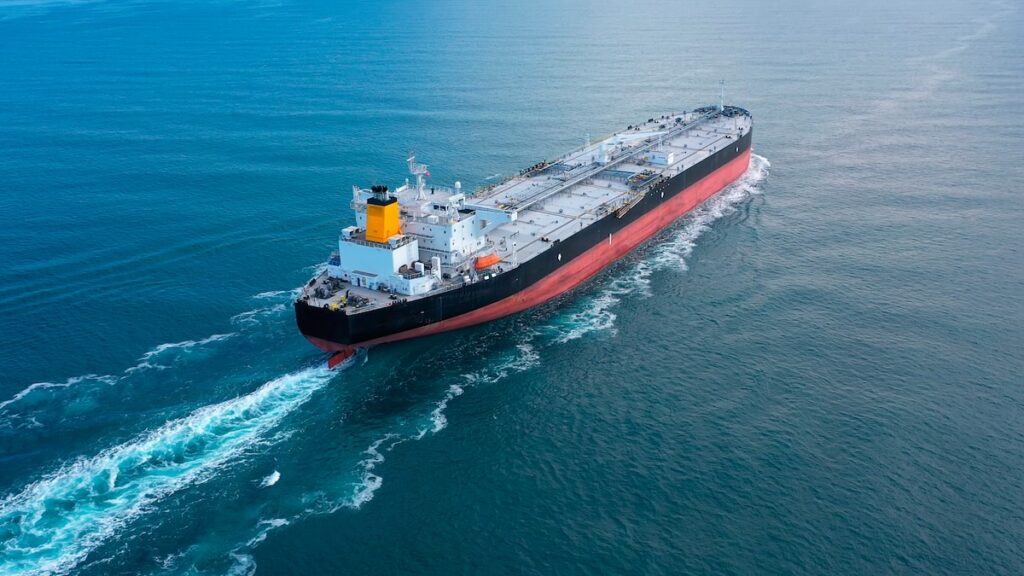
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran.