
A Vietnam-linked threat actor tracked as APT32 is believed to have carried out intrusion campaigns against Chinese entities in an effort to collect intelligence on the COVID-19 crisis, FireEye reports.

Hi, what are you looking for?

A Vietnam-linked threat actor tracked as APT32 is believed to have carried out intrusion campaigns against Chinese entities in an effort to collect intelligence on the COVID-19 crisis, FireEye reports.
Many of my recent conversations have turned toward SD-WAN, especially with adoption growing at such an impressive rate. According to a recent research from IDC, this is set to continue and could reach $4.5 billion by 2022. The enterprise wants to be efficient and agile, and optimizing cloud connectivity for remote sites and locations is an essential factor in achieving this.
Cybereason Mobile MDR gives enterprises a managed solution that will detect and prevent suspicious activity on mobile devices, while through Cybereason Mobile it provides access to a team of iOS and Android analysts, 24x7x365, for efficient discovery, triaging and mitigation of mobile incidents.
A Chinese threat actor tracked as Evil Eye has updated the tools it uses to target Uyghurs, a minority Turkic ethnic group in the Xinjiang Uyghur Autonomous Region in Northwest China, incident response and threat intelligence firm Volexity reports.
A vulnerability impacting nearly all antivirus products out there could have been exploited to disable anti-malware protection or render the operating system unusable, RACK911 Labs security researchers reveal.
The Mail application in iOS is affected by two critical zero-day vulnerabilities that appear to have been exploited in targeted attacks since at least January 2018, cybersecurity automation company ZecOps reported on Wednesday.
Microsoft issued an out-of-band advisory this week to address Autodesk FBX vulnerabilities in Office, Office 365, and Paint 3D. Multiple bugs that were addressed in the Autodesk FBX software development kit (SDK) earlier this month could lead to code execution and denial of service conditions.
Google on Wednesday warned that nation-backed hackers are exploiting the coronavirus pandemic to target health care organizations and those working to fight the pandemic.
The COVID-19 Health Crisis is Forcing Enterprise Security Teams to Deliver More With Less
Thousands of small business owners reeling from the aggressive measures taken to halt the spread of the coronavirus may have had their personal information exposed last month on a government website that handles disaster loan applications.
A vulnerability in Zoom’s video conferencing service could have been abused to enumerate all of the registered Zoom users within an organization, Cisco Talos reports.
A researcher was able to exfiltrate data from air-gapped computers using vibrations produced by controlling the rotation speed of the machines’ internal fans.
Cybercriminals are taking advantage of the pandemic, including hackers who target hospitals and medical research institutions that are studying the coronavirus, the head of the FBI’s cyber division said Tuesday.
Oil and gas organizations have been targeted in recent spearphishing campaigns using the "Agent Tesla" spyware Trojan, security firm Bitdefender says.
April is a time for tax-related phishing scams, and we haven't been let down this year despite the dominance of COVID-19-themed phishing campaigns. DMARC should stop phishing, right? Not unless the targeted domain itself is spoofed.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Join SecurityWeek today for a virtual summit exploring the strategies and tools organizations need to discover, prioritize, and defend their expanding attack surfaces.
Microsoft fixed vulnerabilities across Azure and AI-branded products, with privilege escalation flaws accounting for the majority.

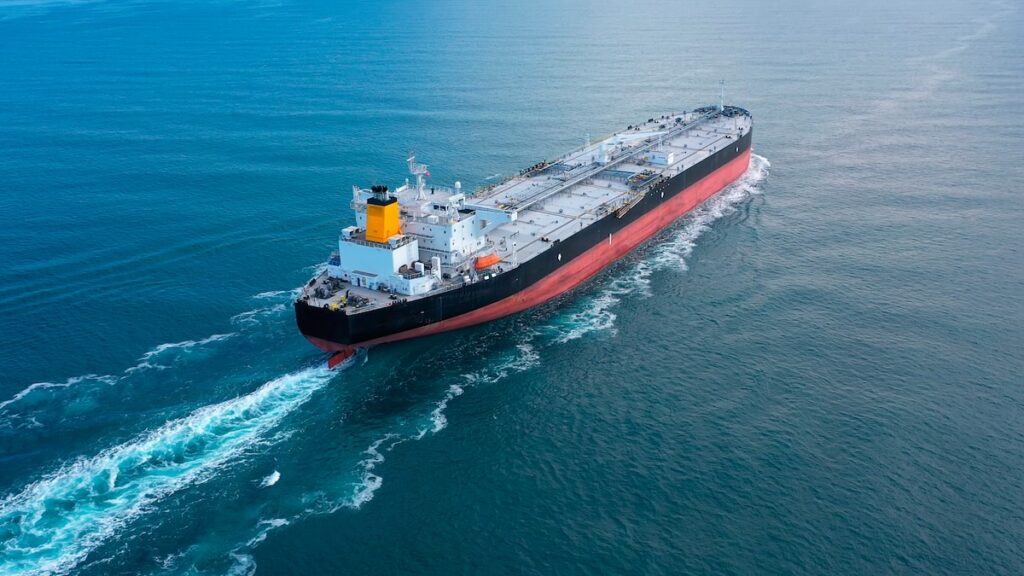
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran.