
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Vulnerabilities

Honeywell Patches Flaws in Tuxedo Touch Home Automation Controller

A researcher has identified two vulnerabilities affecting Honeywell’s Tuxedo Touch automation controllers. The vendor has released a firmware update to patch the security holes.

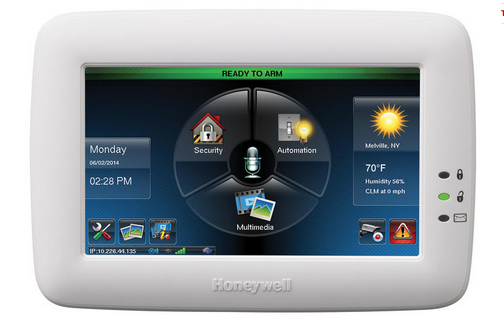
Honeywell Tuxedo Touch is designed to allow users to control cameras, thermostats, lights, shades, and locks via a touchscreen or voice commands.
A researcher has identified two vulnerabilities affecting Honeywell’s Tuxedo Touch automation controllers. The vendor has released a firmware update to patch the security holes.

Honeywell Tuxedo Touch is designed to allow users to control cameras, thermostats, lights, shades, and locks via a touchscreen or voice commands.

Honeywell Tuxedo Touch

Security researcher Maxim Rupp discovered that the Tuxedo Touch controller is plagued by flaws that can be exploited by an attacker to bypass authentication mechanisms and access restricted pages, and trick legitimate users into issuing various commands.

The authentication bypass flaw (CVE-2015-2847) can be leveraged to defeat the JavaScript checks used by the controller’s web interface to ensure that only authorized users can access restricted pages. The checks can be bypassed simply by ignoring authentication requests from the device.

The second issue (CVE-2015-2848) is a cross-site request forgery (CSRF) vulnerability that can be exploited to issue commands to home automation devices controlled by Tuxedo Touch (e.g. lock or unlock doors). The attack only works if the attacker can trick an authenticated user into executing a malicious request. The attacker’s commands are executed with the privileges of the victim user.

Rupp told SecurityWeek that even an attacker with low skill would be able to exploit the vulnerabilities remotely.

Advertisement. Scroll to continue reading.

The researcher says he has identified roughly 500 vulnerable devices, most of which are located in the United States, with the aid of the Shodan search engine. The expert believes a more thorough search might reveal approximately 1,000 vulnerable systems.

The security bugs have been patched by Honeywell with the release of firmware version TUXW_V5.2.19.0_VA. The flaws affect all prior firmware versions.

These are not the only vulnerabilities identified by Rupp. Advisories published earlier this year by ICS-CERT credit the expert for finding security holes in XZERES wind turbines.


Related: Learn more at the ICS Cyber Security Conference

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Trending

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Learn about Frontier Pace Governance: a practical approach to helping IT operations move at AI speed without sacrificing security, accountability, or operational discipline.

Register

Join as we decipher the world of zero trust and share war stories on securing an organization by eliminating implicit trust and continuously validating every stage of a digital interaction.

Register

People on the Move

Rapid7 has named Rik Ferguson as VP of Security Intelligence.

Cytactic has appointed Tim Brown as CSO.

Scott Simkin has joined Vega as CMO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.




