
Hackers claim to have obtained more than 200 GB of archived data from Australian transportation and logistics giant Toll, and they have already started leaking it after the company refused to pay a ransom.
Toll admitted earlier this month that it was hit by ransomware for the second time this year. The company initially said that the attack, which involved Nefilim ransomware, did not result in any data getting stolen, but it later confirmed that the cybercriminals did manage to steal some files after gaining access to a corporate server.
Toll said the compromised server stored information on current and former employees and details on commercial agreements with enterprise customers, but claimed that customer operational data was not exposed.
Nefilim is designed to encrypt files on infected systems, but its operators are also known to steal data from victims and threaten to make it public if a ransom is not paid.
Toll said it would not be paying the ransom and the cybercriminals announced on Wednesday on their website that they are releasing “part 1” of the stolen files.
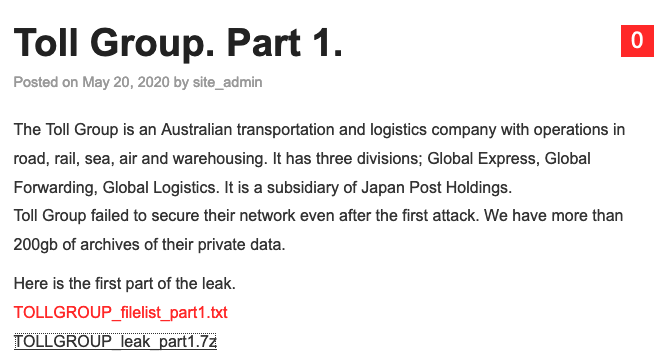
The website set up by the cybercriminals is named “Corporate Leaks” and it can be accessed via the Tor anonymity network. It currently stores information allegedly stolen from seven companies that refused to pay up.
The cybercriminals claim to have stolen more than 200 GB of archived files from Toll and they have so far made available a 2 GB archive.
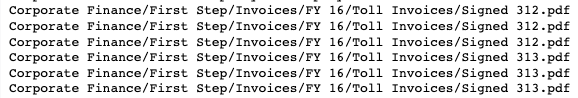
SecurityWeek has seen a list of over 18,000 files that the hackers claim to have stolen from Toll, and these only appear to be the files included in the “part 1” archive. They seem to include various types of financial documents, such as financial reports, board reports, payroll documents, and invoices, going as far back as 2003. However, none of the files in the list appears to be more recent than 2018.
In a statement published on Wednesday, Toll informed customers that “the attacker has now published to the dark web some of the information that was stolen from that server.”
“As a result, we are now focused on assessing and verifying the specific nature of the stolen data that has been published. As this assessment progresses, we will notify any impacted parties as a matter of priority and offer appropriate support,” the company said.
According to its website, Toll has more than 40,000 employees and a global logistics network that spans across 1,200 locations in over 50 countries.
Related: Australian Steel Maker BlueScope Hit by Cyberattack
Related: ATM Maker Diebold Nixdorf Hit by Ransomware
Related: Railway Vehicle Maker Stadler Hit by Malware Attack







You must be logged in to post a comment Login