
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Data Protection

GitHub Now Scans Commits for Atlassian, Dropbox, Discord Tokens

Microsoft-owned GitHub on Monday announced that its token scanning service will also check commits for Atlassian, Dropbox, Discord, Proctorio and Pulumi tokens that have been accidentally shared.

Microsoft-owned GitHub on Monday announced that its token scanning service will also check commits for Atlassian, Dropbox, Discord, Proctorio and Pulumi tokens that have been accidentally shared.

Third-party token scanning was introduced by GitHub in October 2018 and became generally available in May. The service scans public repositories for accidentally committed tokens and alerts the company that issued the token so that it can be revoked before it’s used for malicious purposes.

GitHub initially scanned commits for token formats associated with Alibaba Cloud, AWS, Azure, Google, Mailgun, npm, Slack, Stripe and Twilio. The company said on Monday that it has also added Atlassian, Dropbox, Discord, Proctorio and Pulumi to the list of partners.

“Now if you accidentally check in a token for products like JIRA or Discord, the provider gets notified about a potential match within seconds of check-in, allowing them to revoke the token before it’s used maliciously,” explained Justin Hutchings, senior product manager at GitHub.
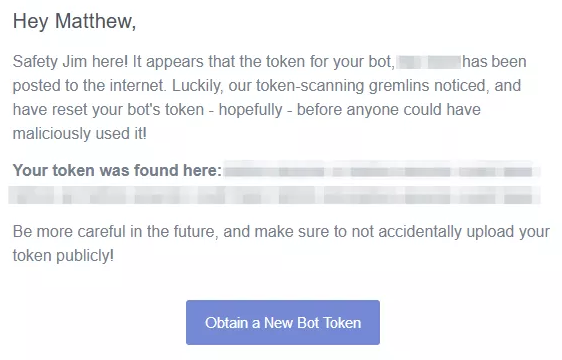
GitHub exposed token warning

According to GitHub, roughly one billion tokens have been sent to its scanning partners for validation since the launch of the service.

The company has advised cloud and API service providers interested in ensuring that their tokens don’t become compromised to reach out and sign up to become a partner. The process involves defining a regular expression to match their token format, setting up an API endpoint, and some paperwork.

Advertisement. Scroll to continue reading.

Related: Slack Tokens Leaked on GitHub Put Companies at Risk

Related: Leaked GitHub API Token Exposed Homebrew Software Repositories

Related: GitHub Adds New Tools to Help Developers Secure Code

Related: Cybercriminals Using GitHub to Host Phishing Kits

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Fredrick Lee has joined Vanta as CISO.

Allie Mellen joined Microsoft as Principal Director, Security Research and Threat Intelligence.

Cohere has appointed Jaya Baloo as CISO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





