
Electrical substations and other power supply facilities are exposed to hacker attacks due to several potentially serious vulnerabilities discovered by researchers in some Siemens protection relays.
On March 8, Siemens and ICS-CERT published advisories to warn organizations of the existence of three vulnerabilities in SIPROTEC 4, SIPROTEC Compact, and Reyrolle devices, which provide integrated protection, control, measurement, and automation functions for electrical substations and other applications. The vendor has released patches and mitigations for each of the flaws.
Positive Technologies, the company whose researchers discovered the flaws, has now provided information regarding the risk and impact.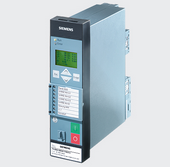
One of the vulnerabilities, tracked as CVE-2018-4840 and rated high severity, can be exploited by a remote and unauthenticated attacker to modify the device’s configuration and overwrite access passwords.
Another security hole, CVE-2018-4839, is a medium severity issue that allows a local or network attacker to recover the access authorization password by intercepting network traffic or obtaining data from the targeted device. The password can be used to gain complete access to a relay, Positive Technologies said.
CVE-2018-4840 and CVE-2018-4839 impact SIPROTEC 4 and SIPROTEC Compact protection relays, specifically the EN100 Ethernet modules and the DIGSI 4 operation and configuration software used by the devices.
Positive Technologies also informed Siemens of CVE-2018-4838, a high severity vulnerability in the web interface that allows an unauthenticated attacker to downgrade the firmware on a device to a version that contains known flaws. This security hole affects SIPROTEC 4, SIPROTEC Compact, and Reyrolle relays that use EN100 modules.
Learn More at SecurityWeek’s ICS Cyber Security Conference
According to Positive Technologies, these vulnerabilities can pose a serious risk to electrical facilities and their exploitation could even result in power supply disruptions.
“By exploiting these vulnerabilities, an attacker is able to change the configuration of power-system protection relay which can lead to disruption of the power equipment protection function (and potentially to an accident) or customer curtailment,” the security firm warned.
Malicious actors targeting SIPROTEC relays is not unheard of. While analyzing the piece of malware known as Industroyer and Crashoverride, which is believed to have been used in the December 2016 attack aimed at an electrical substation in Ukraine, researchers discovered a denial-of-service (DoS) tool that exploits a SIPROTEC vulnerability patched in 2015 to cause relays to become unresponsive.
Related: Energy Regulator Acts to Improve Power Grid Security
Related: Utilities Fear Cyberattacks Could Cause Electric Grid Disruptions
Related: Critical Flaw in GE Protection Relays Exposes Power Grid







You must be logged in to post a comment Login