
Researchers at Cisco have come across a campaign in which malicious actors sent out bogus Microsoft Volume Licensing Service Center (VLSC) emails in an effort to trick corporate users into installing a piece of malware.
The attack starts with a legitimate-looking email informing recipients that they have been assigned administrator permissions on the Microsoft VLSC website. The messages instruct users to click on a link that apparently points to the VLSC.
The VLSC is designed to allow organizations to easily manage their licenses. Customers can use the service to access licensing information, view agreements and purchases, view assigned product keys, and download products.
Because the fake emails look very similar to the ones sent out by Microsoft to customers, and because they have a personalized welcome line, corporate users might click on the link without giving it too much thought. However, the link doesn’t point to the genuine website, but to one of several compromised WordPress sites set up to serve malware. The four websites identified by Cisco were online for roughly six days.
The attackers are using a clever technique to avoid raising any suspicion. The malicious page leverages JavaScript to display the real Microsoft VLSC website. The page then prompts users to download a .ZIP file. Victims will think they are downloading something from Microsoft because the legitimate VLSC is behind the download window, Cisco explained.
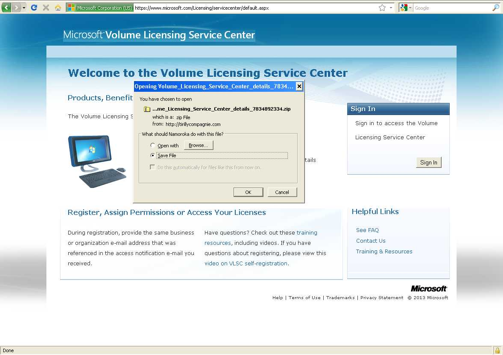
The .ZIP archive contains a file named “Volume_Licensing_Service_Center_ details_7834892334.scr,” a threat detected by antivirus products as Chanitor. Once it’s installed on a system, Chanitor downloads other pieces of malware.
According to Cisco, the variant they have spotted is interesting because it’s capable of evading sandbox analysis.
“The malware seemed to know it was being analyzed and exited after 20 seconds without doing anything,” Cisco’s Martin Nystrom said in a blog post.
After analyzing the malware on real hardware, researchers discovered that the threat is designed to sleep for a total of more than 30 minutes when it’s first executed to prevent sandbox analysis. Once it infects a device, the Trojan attempts to connect to some addresses on the Tor anonymity network.
Cisco says several of its customers downloaded the Trojan, but none of them executed the threat so their systems have not been compromised. On the other hand, this operation shows that malicious actors are targeting corporate users by leveraging improved phishing techniques.






