
Cisco on Thursday announced new patches it has released for the RV320 and RV325 routers to correctly address vulnerabilities that have been targeted in attacks for over two months.
The company attempted to fix the vulnerabilities in January, but the initially released patches were incomplete. Over 9,600 routers were found to be impacted, and all remained exposed due to the incomplete patches.
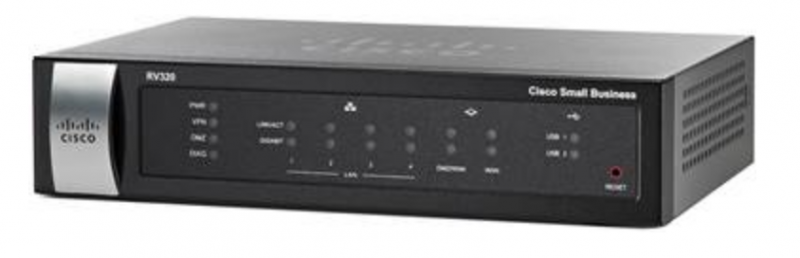 Both vulnerabilities affect the web-based management interface of Cisco Small Business RV320 and RV325 Dual Gigabit WAN VPN routers.
The first of them is tracked as CVE-2019-1653 and could allow an unauthenticated, remote attacker to retrieve sensitive information. The issue is caused by improper access controls for URLs.
“An attacker could exploit this vulnerability by connecting to an affected device via HTTP or HTTPS and requesting specific URLs. A successful exploit could allow the attacker to download the router configuration or detailed diagnostic information,” Cisco explains.
Exploitation of the bug could lead to the second flaw, which is tracked as CVE-2019-1652, and which is due to improper validation of user-supplied input. This could allow an authenticated, remote attacker with administrative privileges on an affected device to execute arbitrary commands.
An attacker could exploit this vulnerability by sending malicious HTTP POST requests to the web-based management interface of an affected device. A successful exploit could allow the attacker to execute arbitrary commands on the underlying Linux shell as root.
Both of these vulnerabilities were found to affect Small Business RV320 and RV325 Dual Gigabit WAN VPN routers running firmware versions 1.4.2.15 through 1.4.2.20 and were addressed with the release of version 1.4.2.22, Cisco says.
No workarounds are available, but disabling the remote management feature (under Firewall > General; this will disable the web-based management interface on the WAN IP address) reduces exposure.
Related: Cisco Improperly Patched Exploited Router Vulnerabilities
Related: Hackers Target Cisco Routers via Recently Patched Flaws
Related: Cisco Patches Critical Vulnerability in Wireless Routers






