
Application Security
Google says it paid out more than $29 million in bug bounty rewards for vulnerability reports received over the past 10 years.
Hi, what are you looking for?

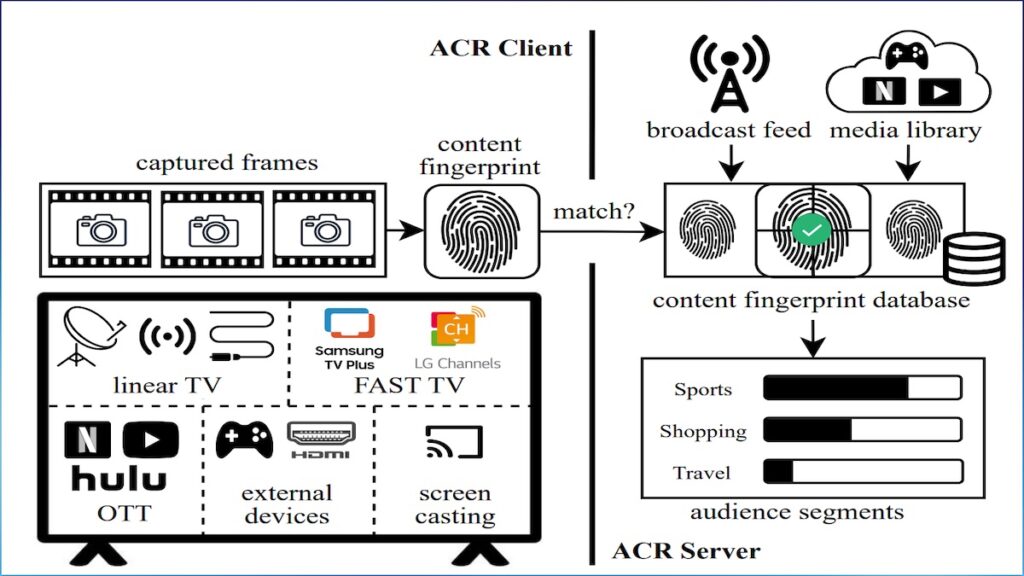
Researchers find Smart TVs from Samsung and LG use a Shazam-like tracker to monitor what you watch. Opting out is complex and time-consuming.
Serial entrepreneurs bank an unusually large seed round to apply process mining techniques to solve security governance problems.
NATO is looking for penetration testing vendors to assess the security of its internet-facing web assets.
Out of the 335 public recommendations on a comprehensive cybersecurity strategy made since 2010, 190 were not implemented by federal agencies as of December...
Google says it paid out more than $29 million in bug bounty rewards for vulnerability reports received over the past 10 years.
Google Cloud this week announced a new set of services aimed at help federal, state, and local government organizations in the United States to...
After years of mostly sitting on the sidelines, Microsoft is starting to be aggressive with cybersecurity acquisitions.The world’s largest software company said Wednesday it...
Juniper Networks has shipped security patches to cover numerous vulnerabilities across its product portfolio, including a series of critical bugs in third-party software used...
Microsoft’s problems with security defects in the Windows Print Spooler utility are getting worse by the week.
Cisco on Thursday released patches for a high severity vulnerability in the Adaptive Security Appliance (ASA) and Firepower Threat Defense (FTD) software, warning that...
A newly uncovered advanced persistent threat (APT) campaign is targeting a large number of users in South Asia, including government entities, according to a...
German software maker SAP has released 12 new security notes as part of its July 2021 security patch day, as well as updates for...
Microsoft’s Patch Tuesday bundle for July 2021 landed with a loud thud as the world’s largest software maker warns of a new wave of...
Microsoft has flexed its muscles in the cybersecurity space, and will drop a reported $500 million in cash to acquire RiskIQ, a late stage...
Security responders at SolarWinds are scrambling to contain a new zero-day vulnerability being actively exploited in what is being described as “limited, targeted attacks.”
The United States Cybersecurity and Infrastructure Security Agency (CISA) has published the results of the Risk and Vulnerability Assessments (RVAs) it conducted in fiscal...
Commercial insurer CNA has started notifying customers that threat actors did have access to some personal data during a ransomware attack in March.
Just days after shipping an emergency Windows update to cover a dangerous code execution flaw (CVE-2021-1675) in the Print Spooler service, Microsoft is investigating...
Cisco this week released patches for high-severity vulnerabilities in Business Process Automation (BPA) and Web Security Appliance (WSA) that expose users to privilege escalation...
The Republican National Committee says none of its data was compromised in a cyberattack that involved B2B IT services provider Synnex.
British anti-malware powerhouse Sophos has acquired Capsule8 to beef up the Linux protection capabilities to its endpoint detection and response product stack.Financial terms of...
Secure Access Service Edge (SASE) provider Versa Networks this week announced it raised $84 million in Series D funding. To date, the company has...
The enterprise asset management space just got a bit more crowded with the launch of Sevco Security, an early-stage startup selling a “cloud-native security...
Security researchers at Microsoft are flagging multiple gaping security holes in firmware shipped on NETGEAR routers, warning that exploitation could lead to identity theft...
AI tools connected to Google Workspace can access millions of sensitive emails and files. Join this session to uncover your organization’s risk and learn a framework to manage AI access.
RegisterJoin as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.
Register
 Where your developers sit on the AI adoption scale has a real impact on how you are addressing security risk.
(Matias Madou)
 Contextual defense helps security teams connect the signals, anticipate what comes next, and stop threats before they escalate.
(Etay Maor)
 As AI accelerates vulnerability discovery and exploitation, so-called virtual patching still comes down to defense-in-depth and strong application security fundamentals.
(Joshua Goldfarb)
 - AI, supply-chain exposure, quantum computing and geopolitical conflict are testing security programs. Preparing for disruption must become part of day-to-day operations.
(Steve Durbin)
 Agentic remediation is not an act of faith. We are talking about fixing known problems, not judgment calls about unfamiliar risk.
(Nadir Izrael)