
Yubico is in the process of replacing YubiKey FIPS (Federal Information Processing Standards) security keys following the discovery of a potentially serious cryptography-related issue that can cause RSA keys and ECDSA signatures generated on these devices to have reduced strength.
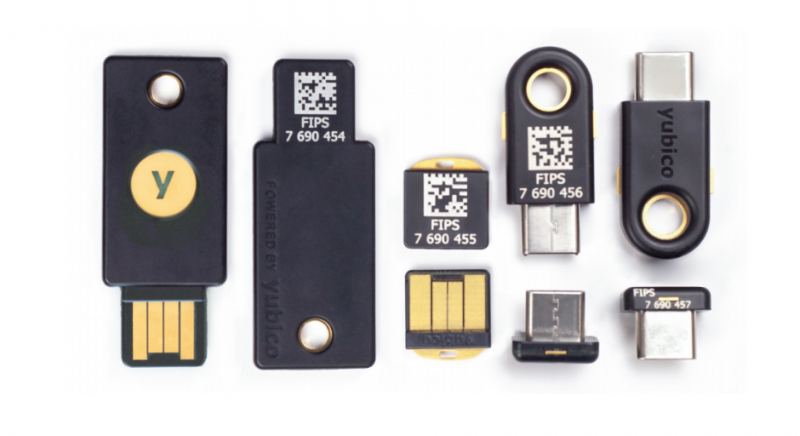
In a security advisory published on Thursday, the company informed customers that the issue impacts YubiKey FIPS series devices running versions 4.4.2 and 4.4.4 of the firmware (version 4.4.3 does not exist), including Nano FIPS, C FIPS and C Nano FIPS devices. No other Yubico products appear to be impacted.
“[Random] values leveraged in some YubiKey FIPS applications contain reduced randomness for the first operations performed after YubiKey FIPS power-up. The buffer holding random values contains some predictable content left over from the FIPS power-up self-tests which could affect cryptographic operations which require random data until the predictable content is exhausted,” Yubico said in its advisory.
“This issue occurs only during the power-up of the YubiKey FIPS Series, version 4.4.2 or 4.4.4. After the predictable content in the random buffer is consumed, the buffer will be filled with the intended full random number generator output, and all subsequent use of randomness will not be affected,” it added.
The issue impacts PIV smart card applications, Universal 2nd Factor (U2F) authentication, OATH one-time passwords, and OpenPGP.
The flaw was discovered internally by Yubico in mid-March and it was patched with the release of firmware version 4.4.5, which received FIPS certification on April 30. The vendor says it’s not aware of any incidents exploiting this weakness.
Yubico has actively reached out to customers to inform them of the free device replacement and says a majority of the affected security keys have already been replaced or are in the process of being replaced. Users who have not heard from the company have been advised to visit a replacement portal set up for this purpose.
The news comes just weeks after Google announced that it was replacing its T1 and T2 Titan Security Key dongles due to a misconfiguration in the Bluetooth pairing protocols.
Related: Support for FIDO2 Passwordless Authentication Added to Android
Related: Android’s Security Key Now Works with iOS Devices
Related: New Authentication Standard Coming to Major Web Browsers






