
Several critical and high-severity vulnerabilities have been identified in programmable logic controller (PLC) and human-machine interface (HMI) products made by WAGO, a German company specializing in electrical connection and automation solutions.
According to an advisory published this week by Germany’s CERT@VDE, which coordinates cybersecurity issues related to industrial automation, WAGO’s PFC100 and PFC200 PLCs, its Edge Controller product, and Touch Panel 600 HMIs are affected by four memory-related flaws impacting the iocheckd service I/O-Check.
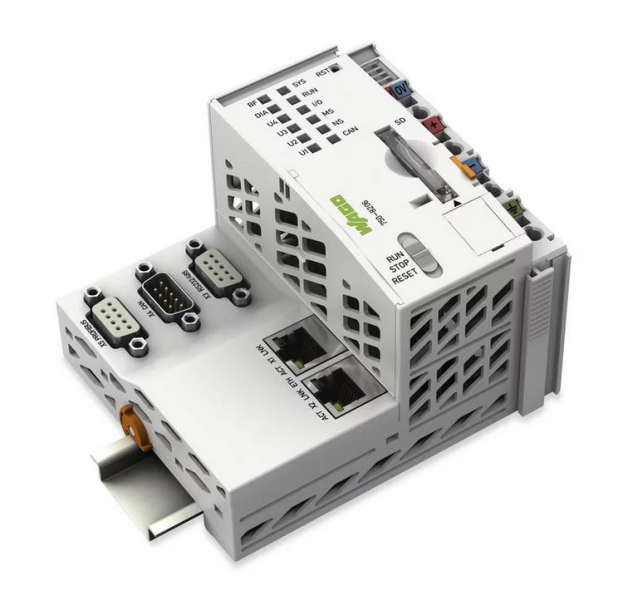 The security holes can allow an attacker to cause a denial of service (DoS) condition and in some cases even execute arbitrary code. Each vulnerability can be exploited by sending specially crafted packets containing OS commands to the targeted device.
Uri Katz, protocol researcher at industrial cybersecurity firm Claroty, has been credited for reporting the flaws to the vendor.
“By chaining the shared memory overflow vulnerability (CVE-2021-34566) and the out-of-bound read vulnerability (CVE-2021-34567), we were able to create a full blown pre-auth remote code execution to take over any WAGO PFC100/200 device remotely,” Katz told SecurityWeek.
Katz noted that there are a few hundred WAGO PFC devices exposed to the internet, which means they can be remotely targeted by malicious actors.
“By exploiting these vulnerabilities, the attacker is potentially able to manipulate or disrupt the device, gain access to the OT network and take over further portions of the network,” Katz explained.
WAGO released patches for these vulnerabilities in June (FW18 Patch 3), and also shared some mitigation advice.
Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series
The vendor noted that the impacted I/O-Check service is only needed during the installation and commissioning of devices — it’s not needed during normal operations — and customers have been advised to disable the service after commissioning.
“This is the easiest and securest way to protect your device from the listed vulnerabilities and possible upcoming zero-day exploits,” users have been told.
However, Katz said that while Claroty does not have an exact number, in most cases the I/O Check service is left enabled by organizations.
Related: WAGO Controller Flaws Can Allow Hackers to Disrupt Industrial Processes
Related: Tens of Vulnerabilities Expose WAGO Controllers, HMI Panels to Attacks
Related: Critical Vulnerabilities Found in WAGO Industrial Switches







You must be logged in to post a comment Login