
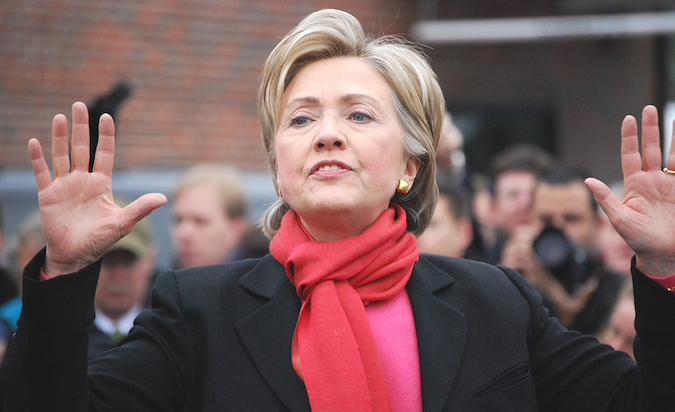
An official inquiry has found serious shortcomings in how US presidential candidate Hillary Clinton and her predecessors in her former post as secretary of state managed the security of their emails.
A report made public Wednesday by the State Department’s independent inspector general found “longstanding, systemic weaknesses related to electronic records and communications” in the office of the secretary.
Clinton is the frontrunner to secure the Democratic Party nomination to run in November’s presidential election, but her campaign has been dogged by criticism of her decision to conduct diplomatic business on a private email account.
Wednesday’s report will do nothing to reassure her critics, who allege that, by storing her communications on a non-government server, she put national secrets at the mercy of hackers and foreign cyber-attackers.
While the Office of the Inspector General found that Clinton’s Republican predecessor Colin Powell had also used only a private account, it said that Clinton did so even after more up-to-date cyber security guidelines had been issued.
According to the report, when Clinton became secretary of state in 2009, the department’s Foreign Affairs Manual (FAM) said that normal day-to-day operations should be conducted on an authorized system.
“Yet OIG found no evidence that secretary requested or obtained guidance or approval to conduct official business via a personal email account on her private server,” the report says.
The State Department’s current heads of information security told the inspector general that Clinton had a duty to ask permission to use her personal email account, which they would not have granted because of “security risks.”
Related: Clinton Email Server Vulnerable for 3 Months, Security Firm Says
Related: Feedback Friday: Industry Reactions to Hillary Clinton’s Use of Personal Email
Related: Emails Latest Knock to Clinton Presidential Bid
Related: Clinton and Her Emails – A Saga Weighing on US Election






You must be logged in to post a comment Login