
The US Department of Justice and the Black Lotus Labs team at telecom company Lumen Technologies announced on Friday the takedown of two proxy services powered by a botnet of thousands of hacked devices.
The Justice Department has worked with Lumen and police in the Netherlands and Thailand to dismantle the proxy services named Anyproxy and 5socks. Their domains have been seized and Lumen has disrupted infrastructure by null-routing all traffic to and from known control points.
The DoJ also unsealed an indictment charging four individuals over their alleged role in operating the services. The suspects are Russian nationals Alexey Viktorovich Chertkov (aged 37), Kirill Vladimirovich Morozov (41), and Aleksandr Aleksandrovich Shishkin (36). The fourth suspect is 38-year-old Kazakhstani national Dmitriy Rubtsov.
The suspects appear to be at large and it remains to be seen if they will ever be prosecuted in the United States.
They are accused of using known vulnerabilities to take control of thousands of outdated home routers and IoT devices. The cybercriminals deployed malware that enabled them to abuse the devices for proxy services that could be used to conduct malicious activities without being identified.
Such residential proxy services can be leveraged to conduct ad fraud, brute-force attacks, DDoS attacks, and to take advantage of compromised user data.
“Given the source range, only around 10% are detected as malicious in popular tools such as VirusTotal, meaning they consistently avoid network monitoring tools with a high degree of success,” Black Lotus Labs explained.
The 5socks website has been around for more than 20 years, but only in recent years came to the attention of authorities and the cybersecurity industry. It advertised more than 7,000 proxies worldwide for prices ranging between $10 and $110 (in cryptocurrency) per month. The Russian and Kazakh suspects are believed to have made over $46 million through renting the hacked devices.
While the 5socks site advertised 7,000 proxies, Black Lotus Labs saw roughly 1,000 weekly active proxies across more than 80 countries. However, more than half of the victims were observed in the United States.
By targeting devices that reached end of life (EOL), the cybercriminals were able to obtain bots without the need to exploit zero-day or one-day vulnerabilities.
The FBI last week issued an alert to warn users about the risk of EOL routers getting hacked and abused as proxy servers. The agency shared TheMoon as an example of malware used in such attacks.
The FBI’s alert was likely related to the Anyproxy and 5socks services considering that the law enforcement operation targeting them is named ‘Operation Moonlander’.
According to the DoJ and Black Lotus Labs, the Anyproxy.net and 5socks.net domains were managed by a company based in Virginia and the sites were hosted on servers worldwide. Command and control infrastructure is located in Turkey.
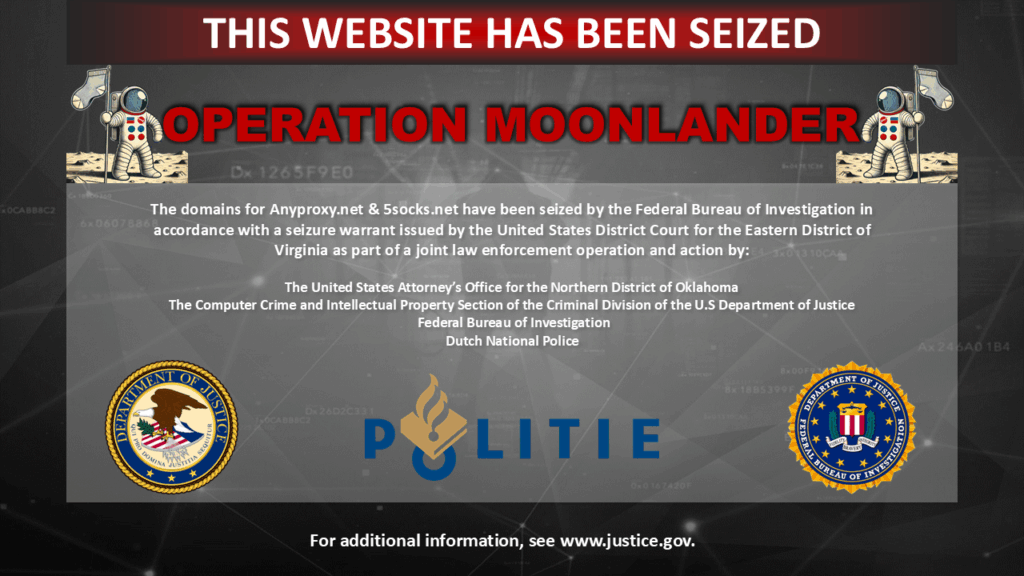
The FBI has seized the domains and foreign law enforcement partners targeted overseas components of the botnet.
Black Lotus Labs has shared indicators of compromise (IoCs) associated with this threat, as well as recommendations for consumers and corporate network defenders. It has not shared any information on the malware itself, as the targeted devices are easy to hack and they could be targeted again by others.
Related: Improperly Patched Samsung MagicINFO Vulnerability Exploited by Botnet
Related: New Eleven11bot DDoS Botnet Powered by 80,000 Hacked Devices






