
Researchers at firmware security company Binarly have identified nearly two dozen vulnerabilities in UEFI firmware code used by the world’s largest device makers.
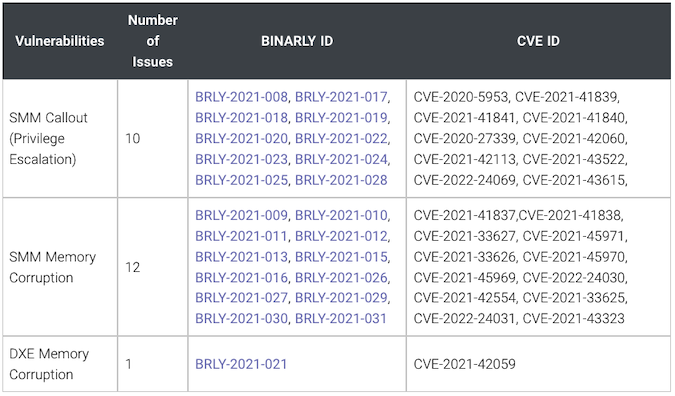
According to Binarly, the 23 high-severity vulnerabilities could impact millions of enterprise devices, such as laptops, servers, routers, network appliances, industrial control systems (ICS), and edge computing devices. There are more than 25 affected vendors, including HP, Lenovo, Fujitsu, Microsoft, Intel, Dell, Bull (Atos) and Siemens.
The security holes exist in the InsydeH2O UEFI firmware provided by Insyde Software.
“The root cause of the problem was found in the reference code associated with InsydeH2O firmware framework code. All of the [impacted] vendors were using Insyde-based firmware SDK to develop their pieces of firmware,” Binarly explained.
The vulnerabilities are mostly related to System Management Mode (SMM) and they can lead to arbitrary code execution with elevated privileges. CVE identifiers have been assigned to each of the 23 weaknesses.
An attacker with privileged user access to the targeted system can exploit the vulnerabilities to install highly persistent malware. The attacker can bypass endpoint security solutions, Secure Boot, and virtualization-based security.
“The active exploitation of all the discovered vulnerabilities can’t be detected by firmware integrity monitoring systems due to limitations of the Trusted Platform Module (TPM) measurement. The remote device health attestation solutions will not detect the affected systems due to the design limitations in visibility of the firmware runtime,” Binarly said.
The vulnerabilities were initially discovered in Fujitsu devices, but a closer analysis revealed that it was a broader issue impacting Insyde-based firmware. Fujitsu was notified in September and Binarly then worked with CERT/CC and the Linux Vendor Firmware Service (LVFS) to identify and notify other impacted vendors.
Insyde has patched the vulnerabilities and it has released security advisories. However, it will likely take some time until the patches reach affected devices.
Technical details about the flaws will be made available in the upcoming days.
Related: Sophisticated iLOBleed Rootkit Targets HP Servers
Related: Supermicro, Pulse Secure Respond to Trickbot’s Ability to Target Firmware
Related: Driver Vulnerabilities Facilitate Attacks on ATMs, PoS Systems
Related: Serious Vulnerabilities Found in Firmware Used by Many IP Camera Vendors







You must be logged in to post a comment Login