
Virtual Event: Zero Trust Strategies Summit - Watch all Sessions
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Incident Response

Twitter Says Android App Vulnerability Exposed Direct Messages

Twitter informed customers on Wednesday that a vulnerability in its Android app could have been exploited by malicious applications to access private data.

According to the social media giant, the flaw is related to a vulnerability that affects Android 8 and 9, which Google patched in October 2018.

“Our understanding is 96% of people using Twitter for Android already have an Android security patch installed that protects them from this vulnerability. For the other 4%, this vulnerability could allow an attacker, through a malicious app installed on your device, to access private Twitter data on your device (like Direct Messages) by working around Android system permissions that protect against this,” Twitter explained.

The company says there is no evidence that the vulnerability has been exploited, but it cannot completely rule out the possibility so it has decided to take some steps to protect users.

It has updated the Android app to prevent external applications from accessing Twitter data, it has informed potentially impacted users to update the application, it has sent in-app notifications to users who could have been vulnerable to inform them if they need to take any action, and it has been working on making changes that would better protect users against such attacks.
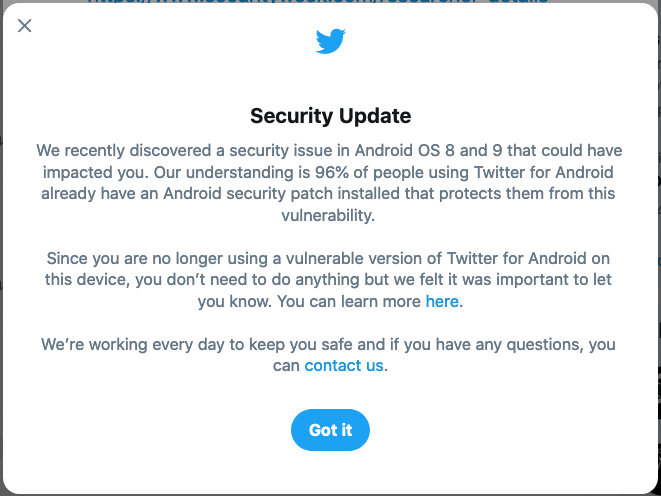
Twitter for Android vulnerability exposed information

Last year, Twitter informed customers that a bug in its Android app led to protected tweets being made public.

Advertisement. Scroll to continue reading.

Other security issues, which the company disclosed in recent months, resulted in personal information being exposed due to the way Firefox stores cached data, and the billing information of businesses being exposed through its ads and analytics services.

Related: Bug Exposed Direct Messages of Millions of Twitter Users

Related: Bug Gives Twitter Apps More Permissions Than Shown

Related: Twitter Suspends Fake Accounts for Exploiting API Vulnerability

Related: Vulnerability in Twitter App Enabled Hackers to Obtain Information, Control Accounts

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

AI tools connected to Google Workspace can access millions of sensitive emails and files. Join this session to uncover your organization’s risk and learn a framework to manage AI access.

Register

Join as we decipher the world of zero trust and share war stories on securing an organization by eliminating implicit trust and continuously validating every stage of a digital interaction.

Register

People on the Move

Randy Resnick has joined IGEL as Field CTO.

Darktrace has named Adam Towns as CFOO, Mike McGuinness as CRO, and Beth Shea as CCO.

Acronis has appointed Gerald Caron as CISO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





