
The Russia-linked threat group known as Turla has been using a sophisticated backdoor to hijack Microsoft Exchange mail servers, ESET reported on Tuesday.
The malware, dubbed LightNeuron, allows the attackers to read and modify any email passing through the compromised mail server, create and send new emails, and block emails to prevent the intended recipients from receiving them.
According to ESET, LightNeuron has been used by Turla — the group is also known as Waterbug, KRYPTON and Venomous Bear — since at least 2014 to target Microsoft Exchange servers. The cybersecurity firm has analyzed a Windows version of the malware, but evidence suggests a Linux version exists as well.
ESET has identified three organizations targeted with LightNeuron, including a Ministry of Foreign Affairs in an Eastern European country, a regional diplomatic organization in the Middle East, and an entity in Brazil. ESET became aware of the Brazilian victim based on a sample uploaded to VirusTotal, but it has not been able to determine what type of organization has been targeted.
The company’s researchers have determined that LightNeuron leverages a persistence technique not used by any other piece of malware, a transport agent. Transport agents are designed to allow users to install custom software on Exchange servers.
The malware runs with the same level of trust as spam filters and other security products, ESET said.
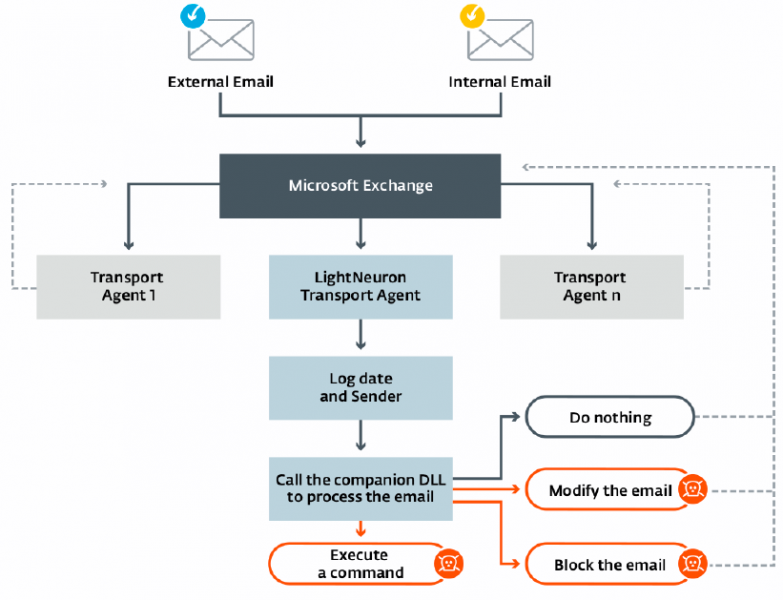
As for command and control (C&C), the malware is controlled by attackers using emails containing specially crafted PDF documents or JPG images. The malware can recognize these emails and extract the commands from the PDF or JPG files.
The commands supported by LightNeuron allow attackers to take complete control of a server, including writing and executing files, deleting files, exfiltrating files, executing processes and commands, and disabling the backdoor for a specified number of minutes.
Last year, ESET detailed a backdoor used by Turla to target Microsoft Outlook. That piece of malware had also used PDF files attached to emails for command and control purposes.
ESET has linked LightNeuron to Turla based on several pieces of evidence, including the presence of known Turla malware on compromised Exchange servers, the use of file names similar to ones known to be used by the group, and the use of a packer exclusively utilized by the threat actor.
In an APT trends report published last year by Kaspersky Lab, the Russian cybersecurity firm also mentioned LightNeuron and attributed it with medium confidence to Turla. Kaspersky had spotted victims in the Middle East and Central Asia.
ESET also noticed that the compromised Exchange servers received commands mostly during work hours in UTC+3, the Moscow time zone. Furthermore, the attackers apparently took a break between December 28, 2018, and January 14, 2019, when many Russians take time off to celebrate the New Year and Christmas.
Related: Turla Cyberspies Use New Dropper in G20 Attacks
Related: Turla-Linked Group Targets Embassies, Ministries
Related: Turla Linked to One of the Earliest Cyberespionage Operations







You must be logged in to post a comment Login