Toyota Germany is notifying customers that their personal information was compromised in a ransomware attack last month.
Initially disclosed in mid-November, the incident impacted the systems of Toyota Financial Services Europe & Africa, a subsidiary of the Japanese carmaker.
Toyota announced last month that the attackers had gained access to internal systems at various locations, and that it took those systems offline in response.
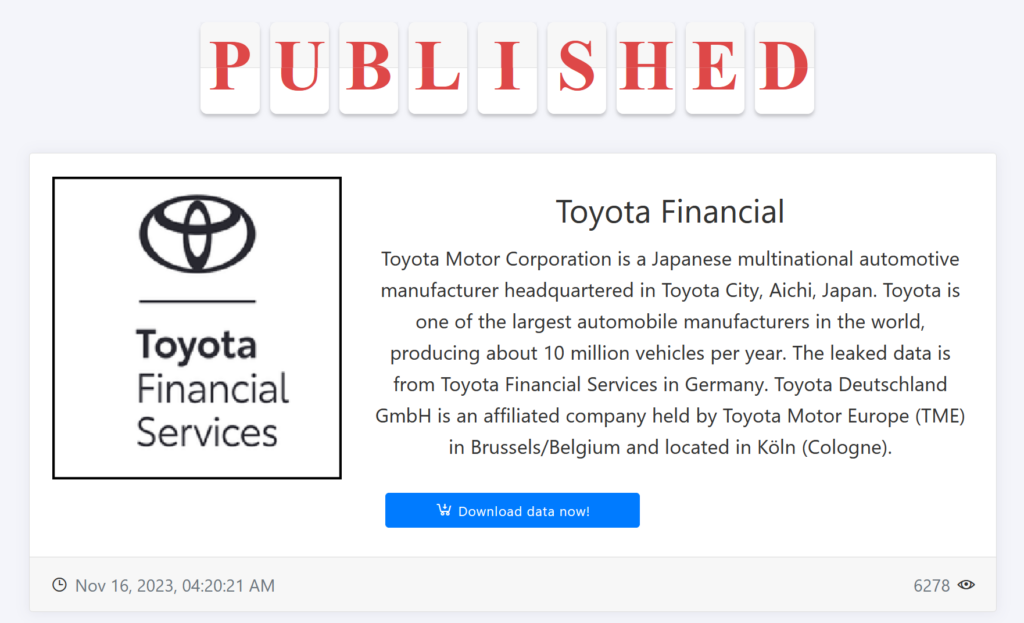
The company did not say what type of attack it fell victim to, but the Medusa ransomware gang quickly claimed responsibility for the incident, adding Toyota Financial Services to its Tor-based leak site and threatening to release stolen data publicly.
Medusa has since published the allegedly stolen information, which includes corporate documents, passport copies, and spreadsheets containing various types of personal information. The ransomware gang also claimed to have accessed user IDs, emails, and hashed passwords.

Last week, Toyota Germany posted an updated notice on its website, informing visitors that the attackers had gained access to the systems of Toyota Kreditbank GmbH, and that personal information was compromised, without providing details on the types of stolen data.
However, the Toyota subsidiary also started mailing out notification letters to the impacted customers, informing them that their personal information, including names, addresses, IBANs, and other information, was compromised in the attack, German news outlet Heise reports.
In its online notice, Toyota also said that it has been gradually restarting Toyota Kreditbank’s systems, but shared no other details on the restoration efforts or on the extent of the attack.
According to security researchers, the recent Citrix NetScaler vulnerability called CitrixBleed (Citrix Bleed) might have been exploited for initial access to Toyota Financial Services’ systems. Various threat actors, including ransomware groups, have been observed targeting the bug in attacks.
Related: Toyota Discloses New Data Breach Involving Vehicle, Customer Information
Related: Toyota: Data on More Than 2 Million Vehicles in Japan Were at Risk in Decade-Long Breach
Related: Vulnerability in Toyota Management Platform Provided Access to Customer Data