The Department of Homeland Security has warned that encrypted traffic sent to and from RuggedCom network products can be decrypted by malicious attackers.
The vulnerability with the proof-of-concept code was publicly disclosed by security researcher Justin W. Clarke of Cylance, according to the ICS-CERT Alert (PDF) released Aug. 21 by the Industrial Control Systems Cyber Emergency Response Team. The key management issue is remotely exploitable and can result in the user losing control over the machine.
 The RSA Private PKI key for SSL communications between the client or end user and the RuggedCom switch is stored in the Rugged Operating System, according to the alert. Since an attacker has access to the private key, it is possible to send malicious communications to RuggedCom network device.
The vulnerability can be exploited to decrypt SSL traffic between the end user and the device, according to the warning.
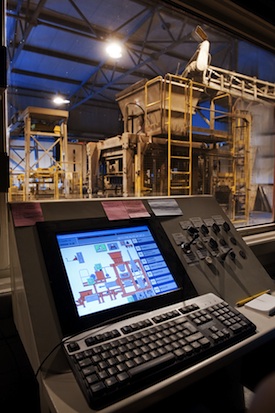
RuggedCom switches and servers are used in “mission-critical” communication networks such as those that make up power grids, railway and traffic control systems, and manufacturing facilities. The hardened equipment is designed to run in any temperature or weather conditions. The switches and servers all run the Rugged Operating System. Customers include defense contractors such as Boeing and Lockheed Martin, as well as utilities and transportation authorities around the country.
This isn’t the first time Clarke has identified issues with RuggedCom products. Earlier this year, Clarke discovered a backdoor login account in all versions of ROS which could not be disabled, nor could the username and password be modified, Clarke found. When RuggedCom didn’t respond to Clarke, he contacted ICS-CERT about his findings, and when the vendor dragged its feet about updating the operating system to close the backdoor, Clarke went public with his findings.
Shortly after Clarke disclosed the presence of the backdoor, RuggedCom released new versions of the firmware to remove the account.
In the latest incident, ICS-CERT has notified RuggedCom and asked the vendor to confirm the vulnerability and identify mitigations, the warning said. While the vendor hasn’t released anything, the ICS alert provides early notice and “baseline mitigations.”
Control system devices should not directly face the Internet, the alert said.
Many organizations put control systems on the Internet because it is easier to manage remotely, Jacob Kitchel, senior manager of security and compliance at Industrial Defender, told Security Week. Organizations have to balance the convenience of managing systems with the security implications, he said.
Users should take defensive measures” such as minimizing network exposure for all control system devices, according to ICS-CERT. Control system networks and devices should be deployed behind a firewall and isolated from the rest of the business.
Finally, all remote access to the control systems should require secure access, such as using a Virtual Private Network, in order to connect.
Related Reading: A New Cyber Security Model for SCADA
Related Reading: ICS-CERT Report Shows Spike in Critical Infrastructure Cyber Attacks
Related Reading: ICS-CERT Updates Security Guidance for Critical Infrastructure
Related Reading: Addressing SCADA Endpoint Protection Concerns
Related Reading: Putting SCADA Protection on the Radar