
Researchers have published proof-of-concept (PoC) exploits to demonstrate that the Windows vulnerability tracked as SMBGhost and CVE-2020-0796 can be exploited for local privilege escalation.
Microsoft says the vulnerability, which it patched on March 12 with an out-of-band update, can be exploited for remote code execution on SMB clients and servers. The critical flaw, described as “wormable” and related to the way SMB 3.1.1 handles certain requests, affects Windows 10 and Windows Server versions 1903 and 1909.
In attacks aimed at SMB servers, the attacker needs to send specially crafted packets to the targeted system. In the case of clients, the attacker has to convince the targeted user to connect to a malicious SMBv3 server.
Researchers have already created tools that can be used to scan for vulnerable servers, and released PoC exploits that achieve a DoS condition. A PoC for remote code execution has yet to be made public, but cybersecurity firm ZecOps has developed and released a PoC that shows how SMBGhost can be exploited to escalate privileges to SYSTEM.
Researchers Daniel García Gutiérrez and Manuel Blanco Parajón have also made available a PoC that exploits SMBGhost to escalate privileges to SYSTEM.
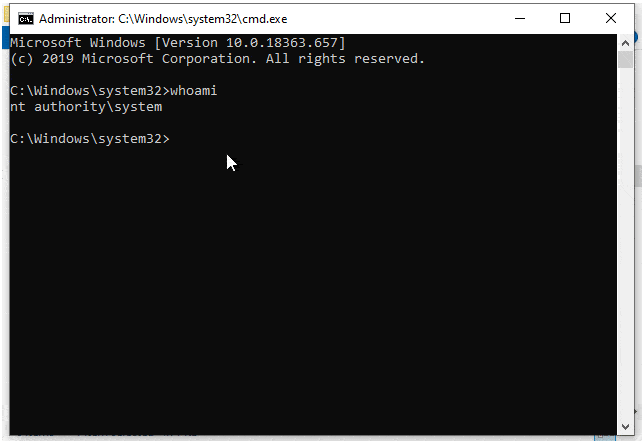
ZecOps has also published a blog post with the technical details for local privilege escalation.
A scan conducted by cybersecurity company Kryptos Logic shortly after CVE-2020-0796 was disclosed revealed the existence of roughly 48,000 servers vulnerable to SMBGhost attacks.
Windows users can protect themselves against potential attacks by applying workarounds and mitigations shared by Microsoft or by installing the official patches. However, some users complained that the Windows update containing the patch had been causing problems.
Related: PoC Exploits Released for Crypto Vulnerability Found by NSA
Related: PoC Exploits Created for Recently Patched ‘BlueGate’ Windows Server Flaws
Related: PoC Exploits Released for Unpatched Edge, IE Vulnerabilities






