
More than 20 vulnerabilities have been identified by Cisco’s Talos research and threat intelligence unit in a Lantronix Wi-Fi module designed for critical industrial and commercial applications.
The affected product, the PremierWave 2050 enterprise Wi-Fi module, delivers always-on 5G Wi-Fi connectivity, and is designed for mission-critical operations. According to the vendor’s website, it delivers enterprise-grade security.
However, Cisco Talos researchers discovered that the product is affected by a total of 21 vulnerabilities, a majority of which have been assigned critical or high severity ratings. Talos has published 18 separate advisories describing the vulnerabilities.
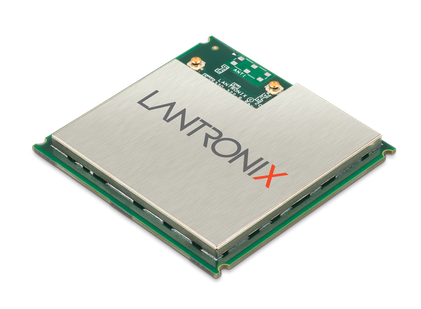 The researchers have reproduced the vulnerabilities on Lantronix PremierWave 2050 version 8.9.0.0R4, and Talos claims there are no official patches for the security holes, despite the vendor knowing about them since June 15.
SecurityWeek has reached out to Lantronix regarding Talos’ findings and will update this article if the company responds.
Lantronix is a California-based company that provides connectivity and engineering services for IoT and Remote Environment Management (REM).
The vulnerabilities discovered by Talos researchers include OS command injection, remote code execution, information disclosure, file overwrite, and local file inclusion.
Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series
A remote attacker can exploit the flaws to completely compromise the PremierWave 2050 operating system. What they can do from there depends on the capabilities of the system the module is embedded in, Matt Wiseman, research engineer at Talos, told SecurityWeek.
“It is difficult to speculate on theoretical real world impacts as this device exists merely to provide wireless connectivity and an execution environment for other systems built on top of it,” Wiseman explained. “The vulnerabilities in the PremierWave 2050 could expose a wide array of other systems to remote compromise. As the data sheet indicates, it is intended for use in ‘sensitive, mission critical, industrial and commercial applications.’ [It] is quite possible for the vulnerable service to be running on a device and the end-user be unaware that their device even contains a Lantronix device.”
“As an example of a potentially vulnerable device, hard-coded strings in the PremierWave 2050 firmware indicate at least one Medical Device Manufacturer is using the Lantronix device, and the location of those strings make it very likely they use the vulnerable service,” the researcher said.
While exploitation of all of these vulnerabilities requires authentication, Wiseman told SecurityWeek that the PremierWave 2050 firmware includes default credentials that can be found online, and it’s up to the third-party device manufacturer or the end-user to change those default credentials.
“The system will notify the administrator of the usage of the default password, but that
notification exists in a configuration page two clicks away from the home page. Given that the PremierWave 2050 is intended as a basis to have some other system built on top of it, it is quite possible the end-user will not make use of, or even be aware of, this interface and therefore not update the password,” he explained.
If the credentials have been changed, it may be possible for an attacker — particularly in older versions — to obtain them by sniffing the traffic of an authenticated user.
UPDATE: Lantronix has provided the following statement to SecurityWeek:
The 18 vulnerability advisories published by Talos have been resolved in firmware v9.10.0.0R4, which was recently released to customers at this link. Customers are formally notified of firmware updates for the PremierWave 2050 through a Process Change Notice process.
The embedded module unit tested by Talos was using firmware v8.9.0.0R4. Any factory reset of the device results in a default password warning on the home/welcome page during a new Quick Start setup process added in v9.9.0.0R4. When applicable, the warning also appears in both the User Management and CLI Configuration pages that provide password change capabilities. The next revision of the firmware will include this warning on the main menu home screen. (Note: Lantronix system level product ships with unique default passwords.)
Lantronix has a long history of managing and securing mobile and IoT devices. Lantronix has established a communication path, via “[email protected],” to enable reporting of vulnerabilities to the company for review/action.
Related: Vulnerabilities in Realtek Wi-Fi Module Expose Many Devices to Remote Attacks
Related: FragAttacks: New Vulnerabilities Expose All Devices With Wi-Fi to Attacks







You must be logged in to post a comment Login