
Rockwell Automation has released a firmware update for its Allen-Bradley Stratix 5900 services router to address tens of vulnerabilities patched over the past few years in Cisco’s IOS software.
The Stratix 5900 is a hardened security router that runs Cisco’s IOS software. According to ICS-CERT, the product is used worldwide in the critical manufacturing, energy, and water and wastewater sectors.
Firmware version 15.6.3 released recently by Rockwell Automation for its Stratix 5900 routers patches more than 60 vulnerabilities discovered in Cisco IOS since March 2014. This means that, for more than three years, organizations using these devices were left exposed to potential attacks exploiting these flaws.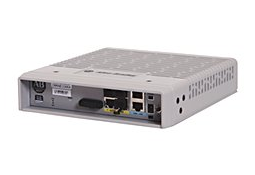
The list of security holes includes improper input validation, authentication, information exposure, path traversal, and resource management vulnerabilities that can be exploited for man-in-the-middle (MitM) attacks, denial-of-service (DoS) attacks, and remote code execution.
A majority of the flaws have been classified as high severity, and they can be exploited remotely without authentication. Cisco has not seen any evidence of exploitation in the wild, but for one vulnerability, tracked as CVE-2016-6415, the hacker group calling itself Shadow Brokers did release an exploit targeting Cisco PIX firewalls. The exploit in question may have been used in attacks by the NSA-linked Equation Group.
Some of the vulnerabilities patched with the latest Stratix 5900 firmware update affect third-party components, such as NTP and OpenSSL.
“Rockwell Automation encourages users of the affected versions to update to the latest available software versions addressing the associated risk, and including improvements to further harden the software and enhance its resilience against similar malicious attacks,” ICS-CERT said in its advisory.
This is the sixth advisory published by ICS-CERT this year for vulnerabilities in Rockwell Automation products. The organization previously disclosed critical, high and medium severity flaws affecting Logix5000, GuardLogix, FlexLogix and CompactLogix controllers, several Stratix switches, the Connected Components Workbench (CCW) software configuration platform, and the FactoryTalk Services Platform.
Related Reading: Rockwell Automation Teams With Claroty on Industrial Network Security
Related Reading: Flaw Allows Attackers to Modify Firmware on Rockwell PLCs
Related Reading: Rockwell Patches Code Execution Flaw in RSLogix Product







You must be logged in to post a comment Login