
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Ransomware

Ransomware Group Claims 100 Gb of Data Stolen From Nissan

The Akira ransomware group has taken credit for the recent attack that impacted Nissan Australia and New Zealand.

Nissan data breach

A known ransomware group has taken credit for the recent cyberattack targeting Nissan and claims to have stolen 100 Gb of information from the Japanese car manufacturer.

The carmaker revealed in early December that internal systems belonging to Nissan Motor Corporation and Nissan Financial Services in Australia and New Zealand had been targeted by hackers. 

It confirmed on December 22 that an “unauthorized third party illegally accessed some of the company’s network systems in Australia and New Zealand” and said it has been working on determining what information is impacted.

Cybersecurity agencies in Australia and New Zealand, as well as privacy regulators and law enforcement, have been notified. 

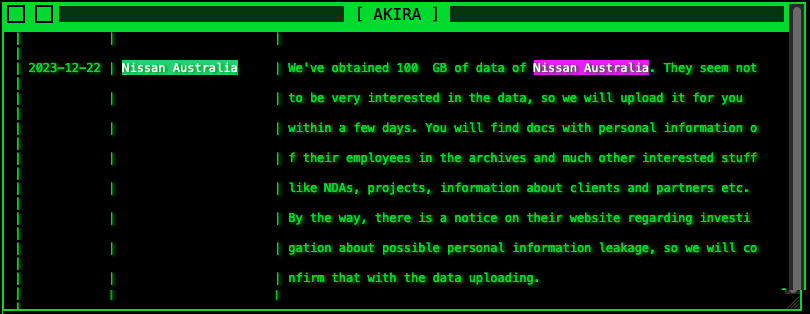
A ransomware group named Akira has taken credit for the attack on Nissan, claiming to have stolen 100 Gb of data, including corporate files and personal information belonging to employees. 

The cybercriminals are threatening to leak the data in the coming days, suggesting that Nissan is not willing to pay the ransom they have demanded.
Advertisement. Scroll to continue reading.

The Akira ransomware operation emerged in March and is believed to have some links to the notorious Conti group. Akira has targeted roughly 180 organizations to date, mostly in the United States.

Nissan is not the only car manufacturer targeted by cybercriminals in recent months. Toyota Germany has also notified customers of a data breach involving their personal information following a ransomware attack. 

Related: 25k Nissan Customers Affected by Data Breach at Third-Party Software Developer

Related: Yamaha Motor Confirms Data Breach Following Ransomware Attack

Related: Toyota Discloses New Data Breach Involving Vehicle, Customer Information

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Trending

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Join as speakers examine the various components of ASM strategy, the push to mandate continuous asset visibility and inventory tools, and the use of red-teaming, bug bounties and pen-tests in modern security programs.

Register

Explore what it takes to operationalize continuous authorization at scale, including the technical, organizational, and cultural changes required.

Register

People on the Move

Doppel has named Joey Rachid as Chief Security Advisor and Field Chief Information Security Officer.

Delinea has appointed Timothy Regan as Chief Financial Officer.

Gwen Gann has become State Chief Information Security Officer for the State of Washington at WaTech.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





