
CONFERENCE CISO Forum Virtual Summit 2026 - View all Sessions
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Vulnerabilities

Patch Released for Actively Exploited GoAnywhere MFT Zero-Day

A patch has been released for the GoAnywhere MFT zero-day vulnerability that has been exploited in attacks.

A patch has been released for the GoAnywhere managed file transfer (MFT) software zero-day vulnerability whose existence came to light recently. News of active exploitation emerged roughly a week ago, but details about the attacks are still not available. 

Fortra, known until recently as HelpSystems, alerted GoAnywhere MFT users on February 1 about a ‘zero-day remote code injection exploit’. The company has since released two other security notifications, each of them providing mitigations and indicators of compromise (IoCs).

GoAnywhere users are now being informed that a patch has been made available. Users are advised to urgently install GoAnywhere MFT 7.1.2.

“Particularly for customers running an admin portal exposed to the Internet, we consider this an urgent matter,” the company said. 
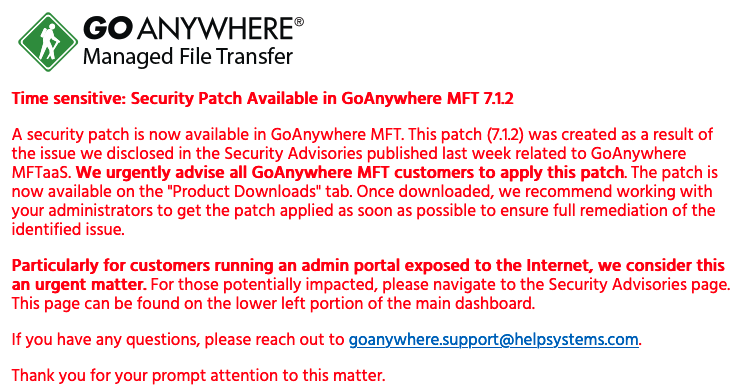
GoAnywhere zero-day patch

There does not appear to be any information about the attacks exploiting the vulnerability. It’s unclear if it has been leveraged by state-sponsored threat actors or profit-driven cybercriminals.  

A CVE identifier has yet to be assigned to the flaw. 

Users have been told to check log files for a particular line that indicates a system has been targeted in an attack exploiting the zero-day vulnerability. If the log files show signs of compromise, users should check their installation for suspicious administrator users.

Advertisement. Scroll to continue reading.

A researcher has published technical details on the flaw, as well as a proof-of-concept (PoC) exploit.

A Shodan search shows nearly 1,000 internet-exposed instances of GoAnywhere. However, the vendor pointed out that exploitation requires access to the application’s admin console, and at least some of the exposed instances appear to be associated with the product’s web client interface, which is not affected. 

Related: Zero-Day Vulnerability Exploited to Hack Over 1,000 Zimbra Email Servers

Related: US Agencies Warn of APTs Exploiting Recent ADSelfService Plus Zero-Day

Related: Accellion Failed to Notify Customers of FTA Zero-Day

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Cohere has appointed Jaya Baloo as CISO.

Jensen Huang has resigned as President and Chief Executive Officer at NVIDIA.

Sean Sweeney has become CIO of the City of Charleston, South Carolina.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





